New Audexa 1.7: Focus mode, smart audit and Sites and group

GRC software for NIS2, DORA, ISO 27001 and the EU AI Act

From audit chaos to operational compliance clarity.

Guided audits, risk treatment, evidence vault, live policies, asset inventory and executive reporting for NIS2, DORA, ISO 27001, ENS, GDPR, the AI Act and more. Built to replace consultant-heavy processes with a repeatable internal system.

1 free ISO 27001 audit to test the platform22 frameworks and 1,763 guided controlsFirst guided audit the same dayPlatform, policies and reports in 5 languages

Comply with major regulations

NIS2DORAISO 27001GDPRAI ActENSISO 22301ISO 27018ISO 42001ISO 9001ISO 14001NIST CSF 2.0TPRMSOC 2ISO 27017ISO 27701ISO 45001ISO 20000-1ISO 37301 / UNE 19601LOPDGDD and LSSICyber Resilience ActWhistleblowing (EU 2019/1937)

New in Audexa 1.7

Audexa centres on your framework and grows with your group.

Two major new features: Focus mode, to work through NIS2, DORA or ISO 27001 step by step, and Sites and group, to run compliance for all your sites and subsidiaries from one place.

Focus mode and smart audit

Only what your framework asks for, with a single next step.

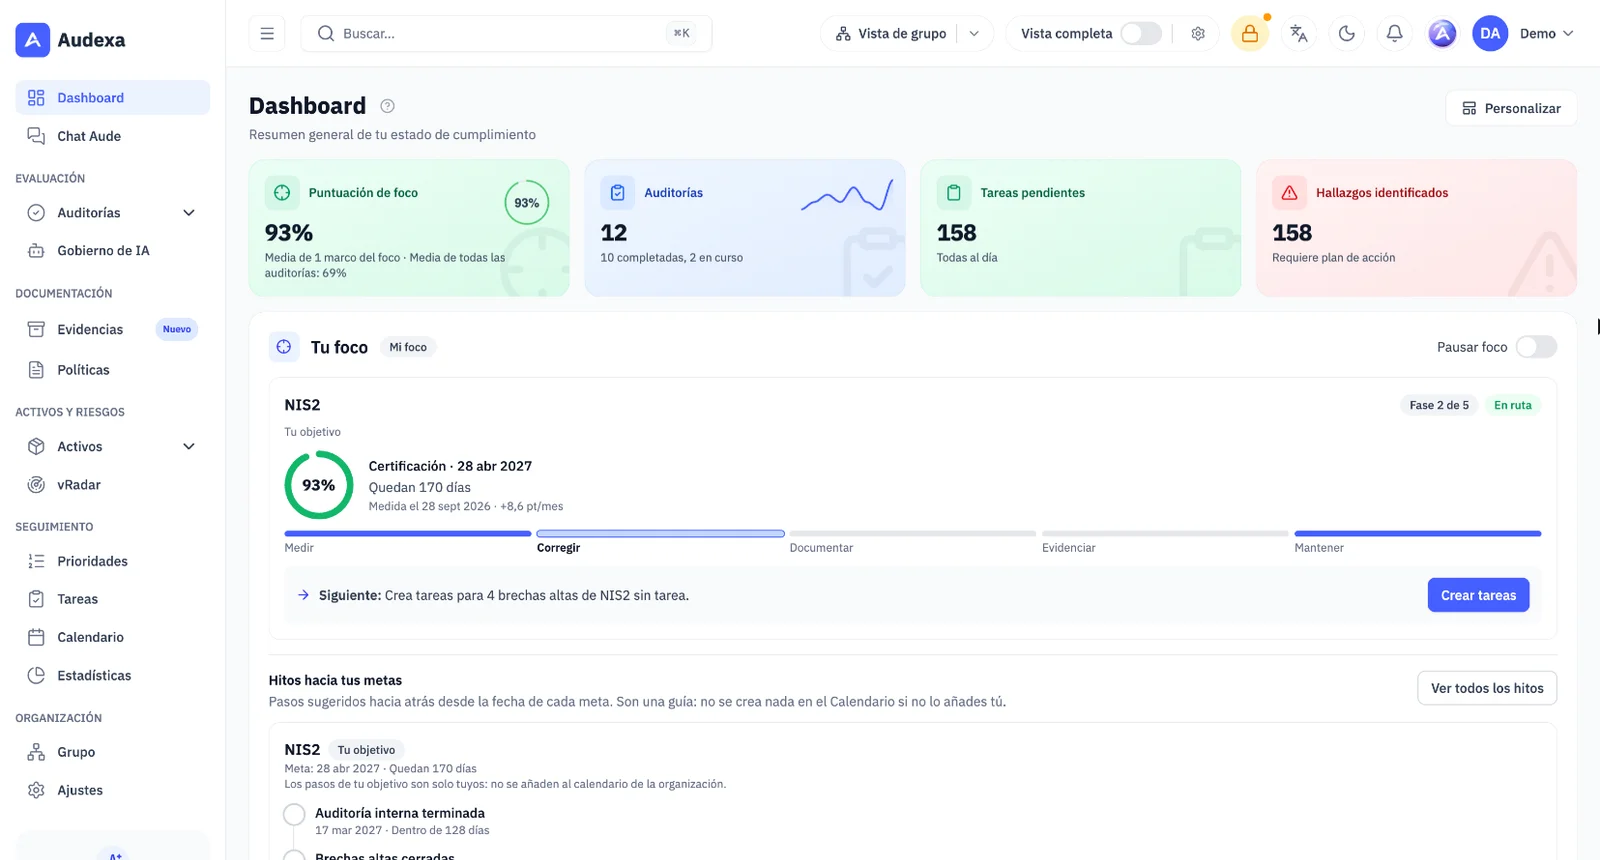
Choose the framework you want to meet and Audexa simplifies itself: Your path tells you which phase you are in and what to do now. When you answer, Audexa suggests answers with their source, shows the exact reference for each question and checks consistency before you submit.

  • Your path: five phases and a next step with the reason for it and how long it takes
  • Exact reference: the NIS2, DORA or ENS article in each question
  • Suggested answers that you accept or change, one by one
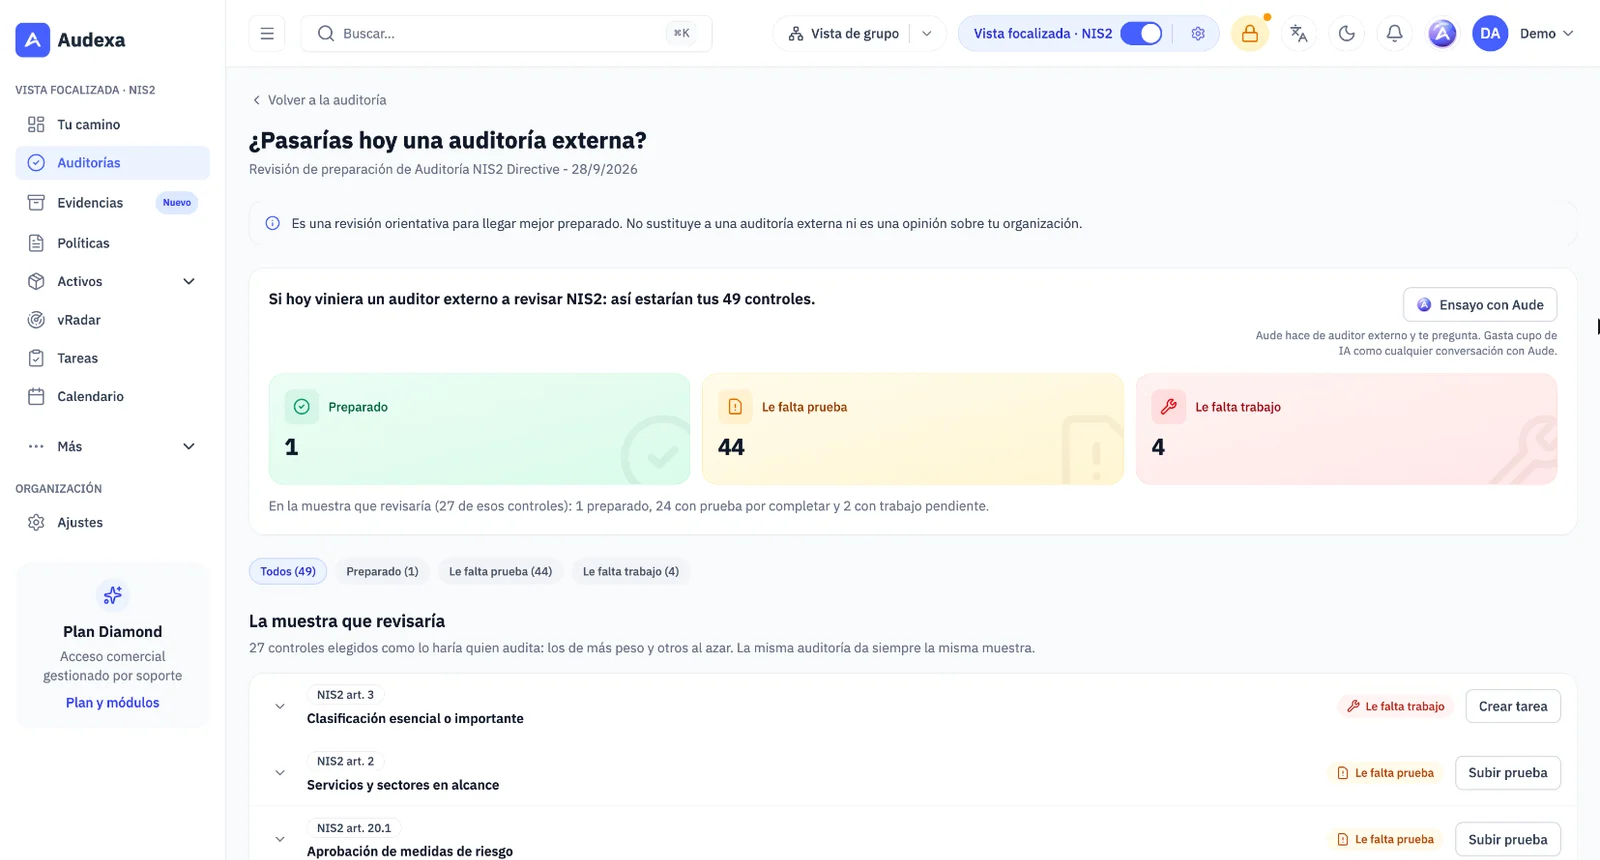
  • Would you pass an external audit today? A guidance review per control

Focused view with one framework on every plan; several frameworks, goals and milestones from Premium.

Discover Focus mode
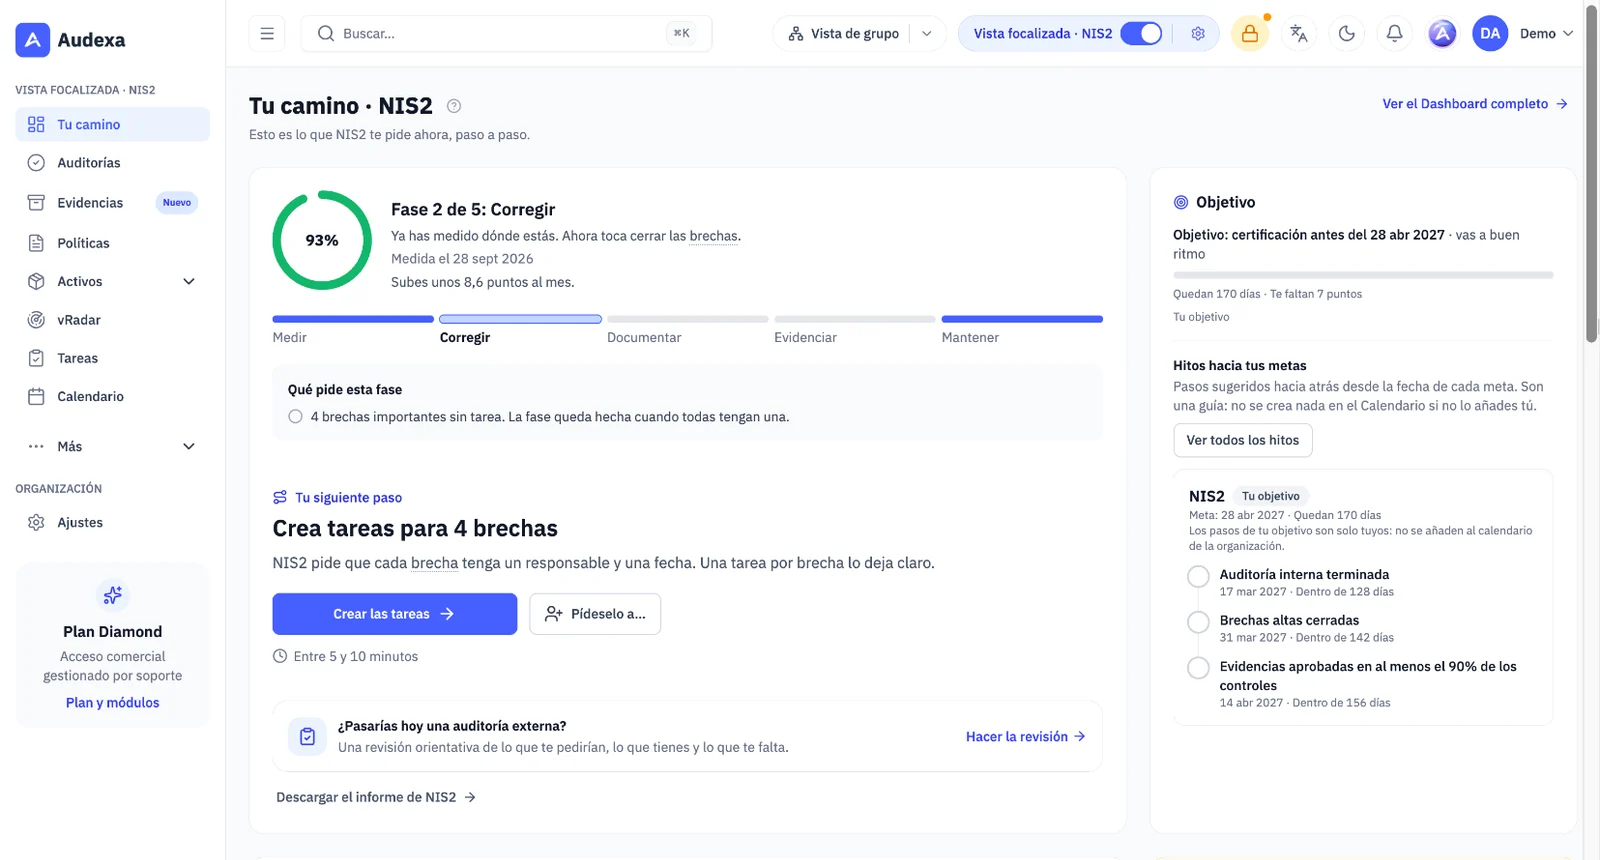
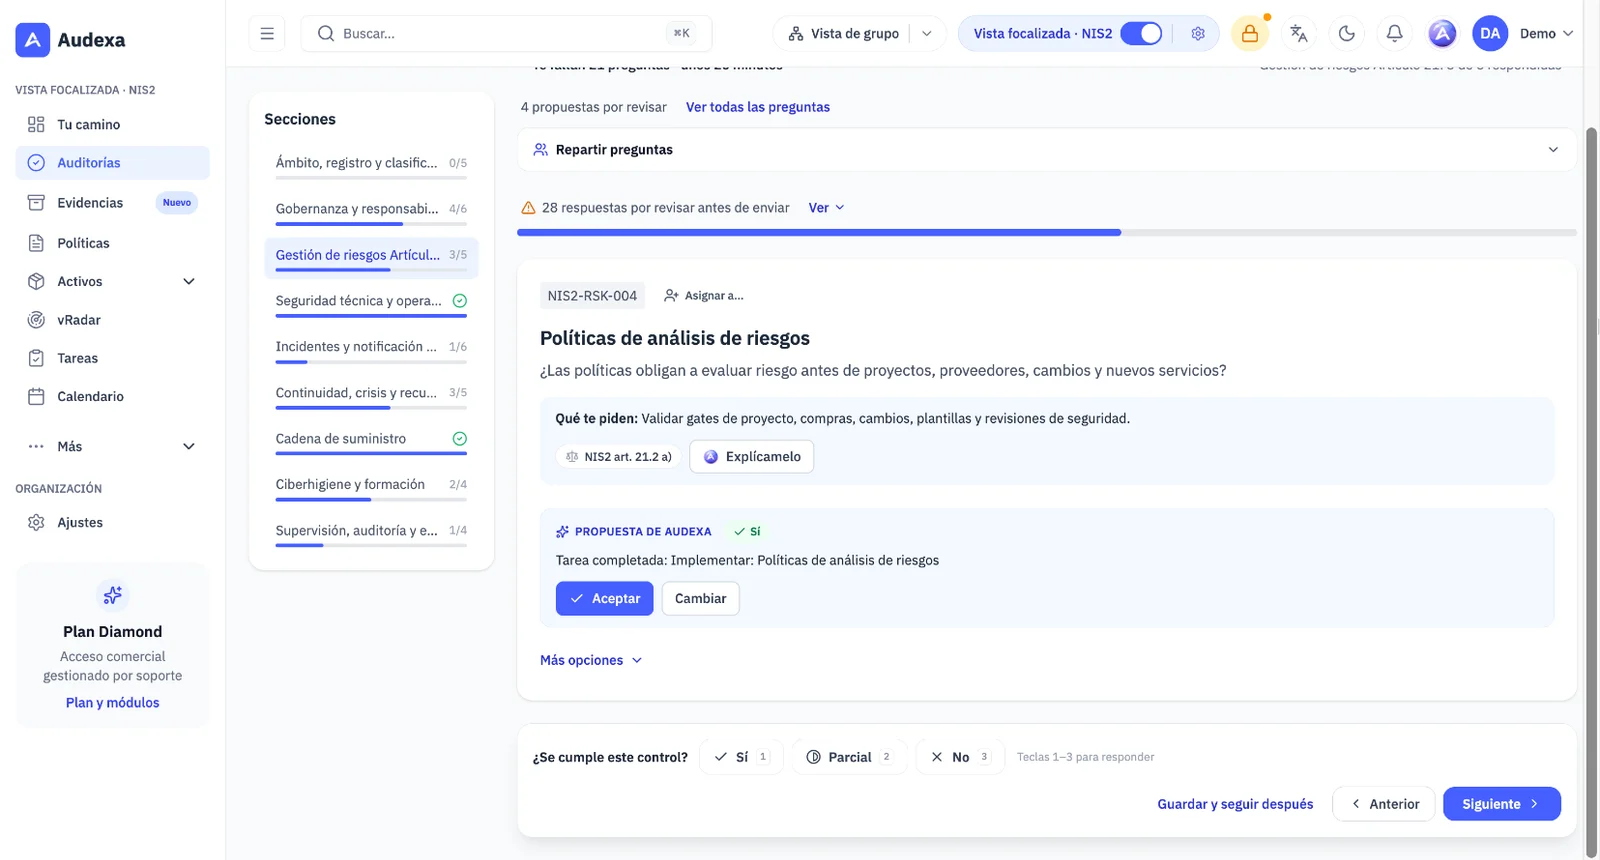
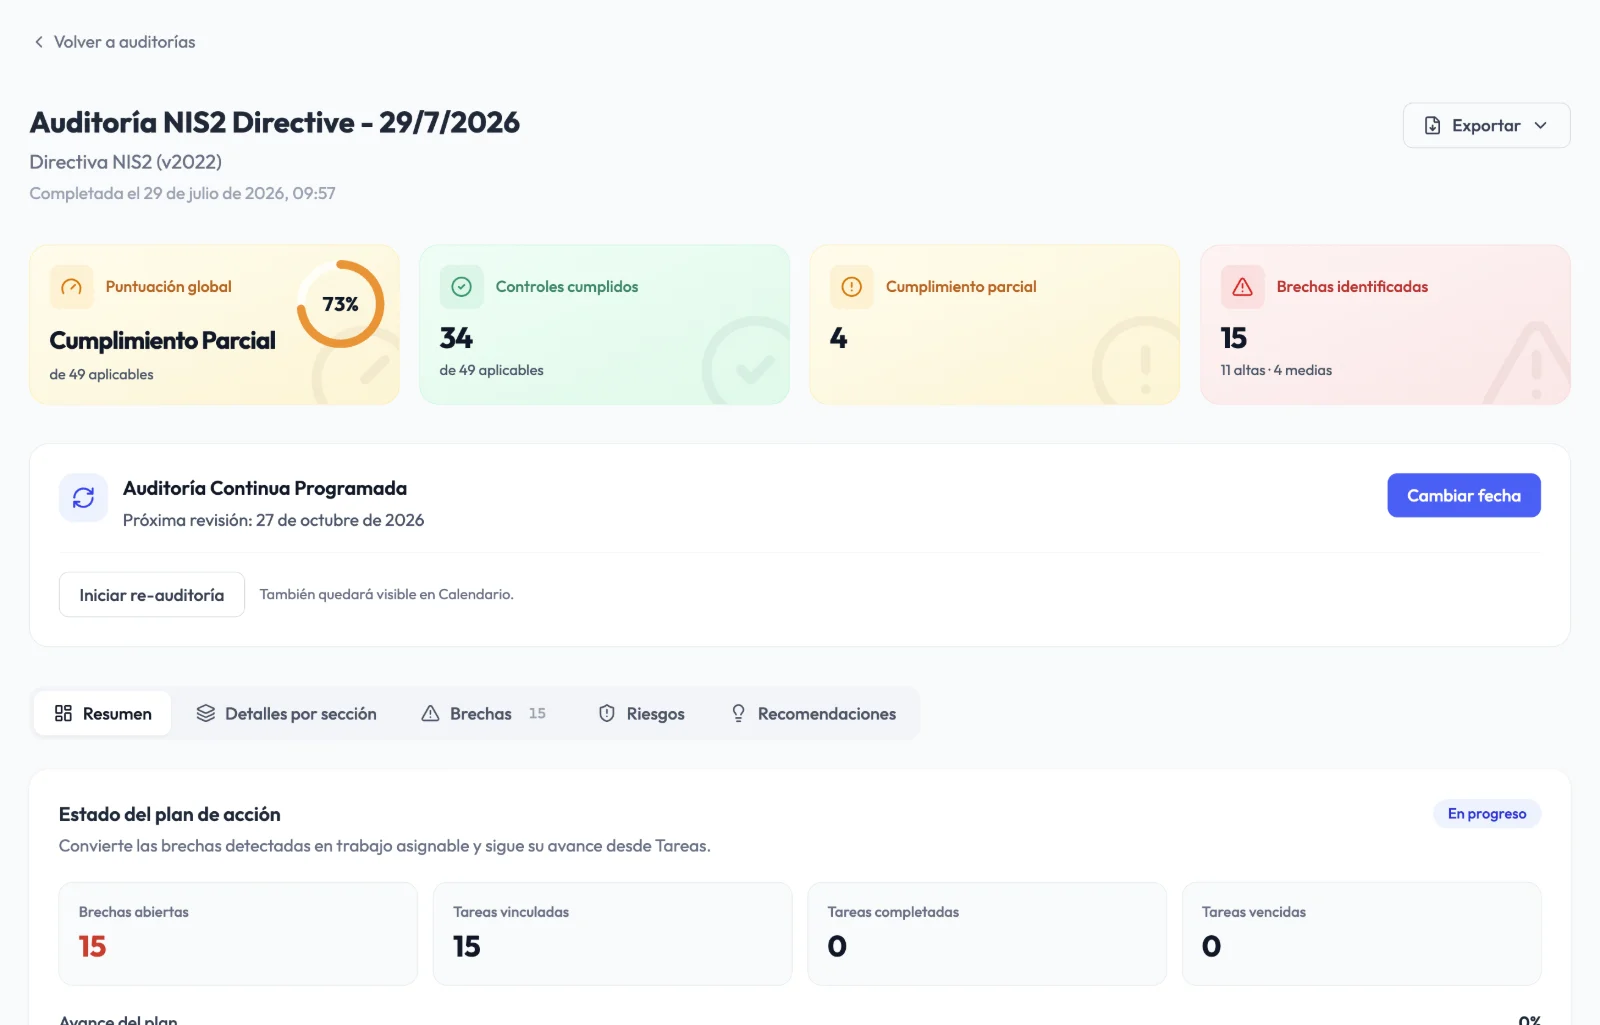
Your NIS2 path in Audexa: phase 2 of 5, next step and goal with milestones
Your path: the phase you are in, what it asks for and your next step.

Sites and group

All your sites and subsidiaries, in a single platform.

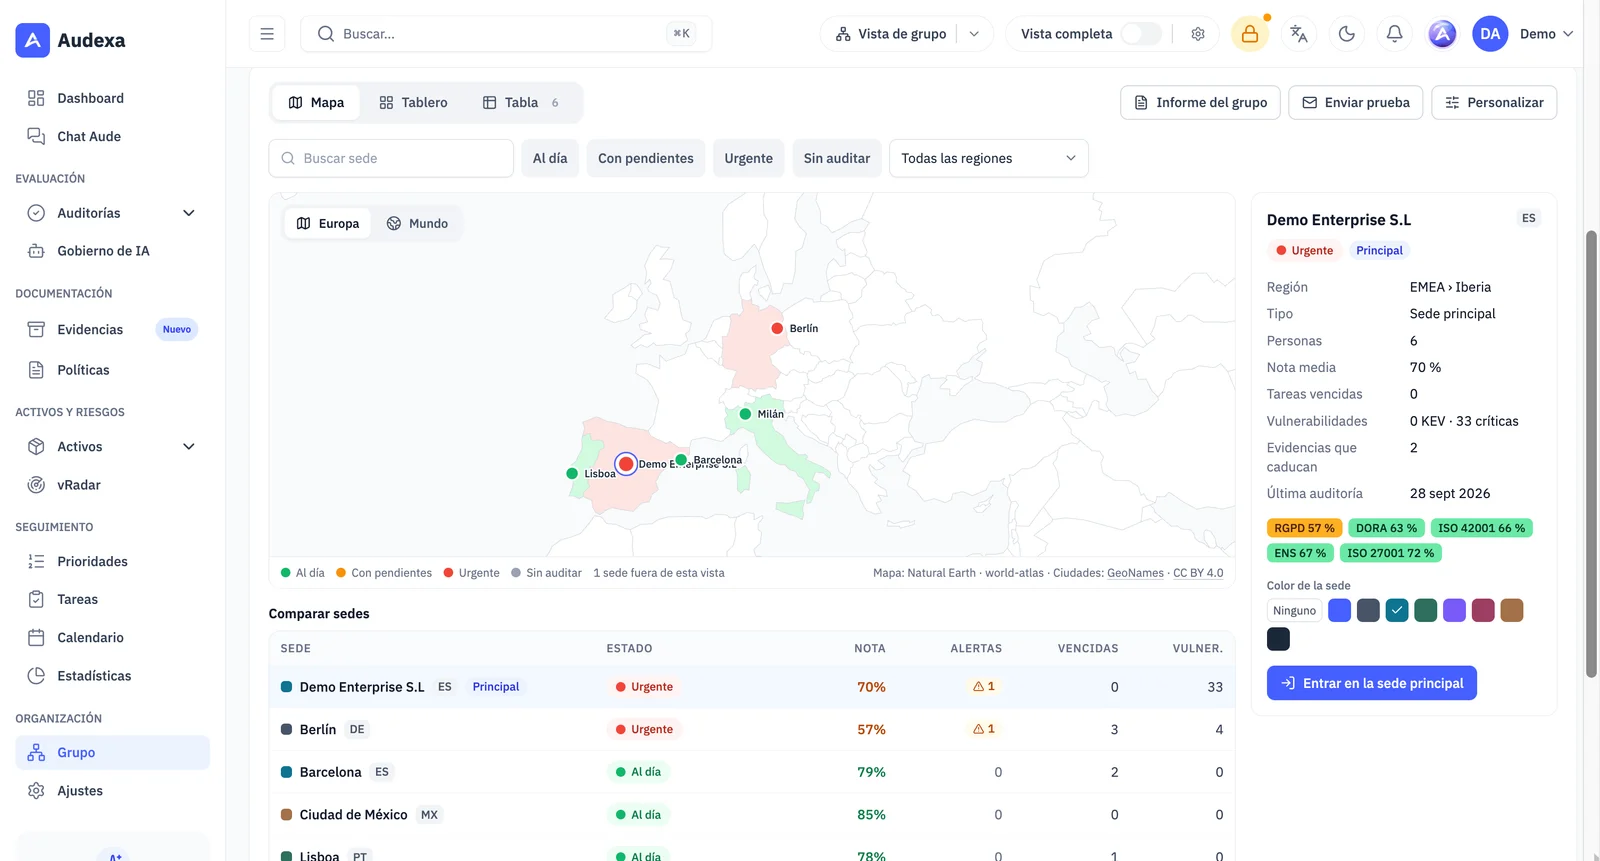
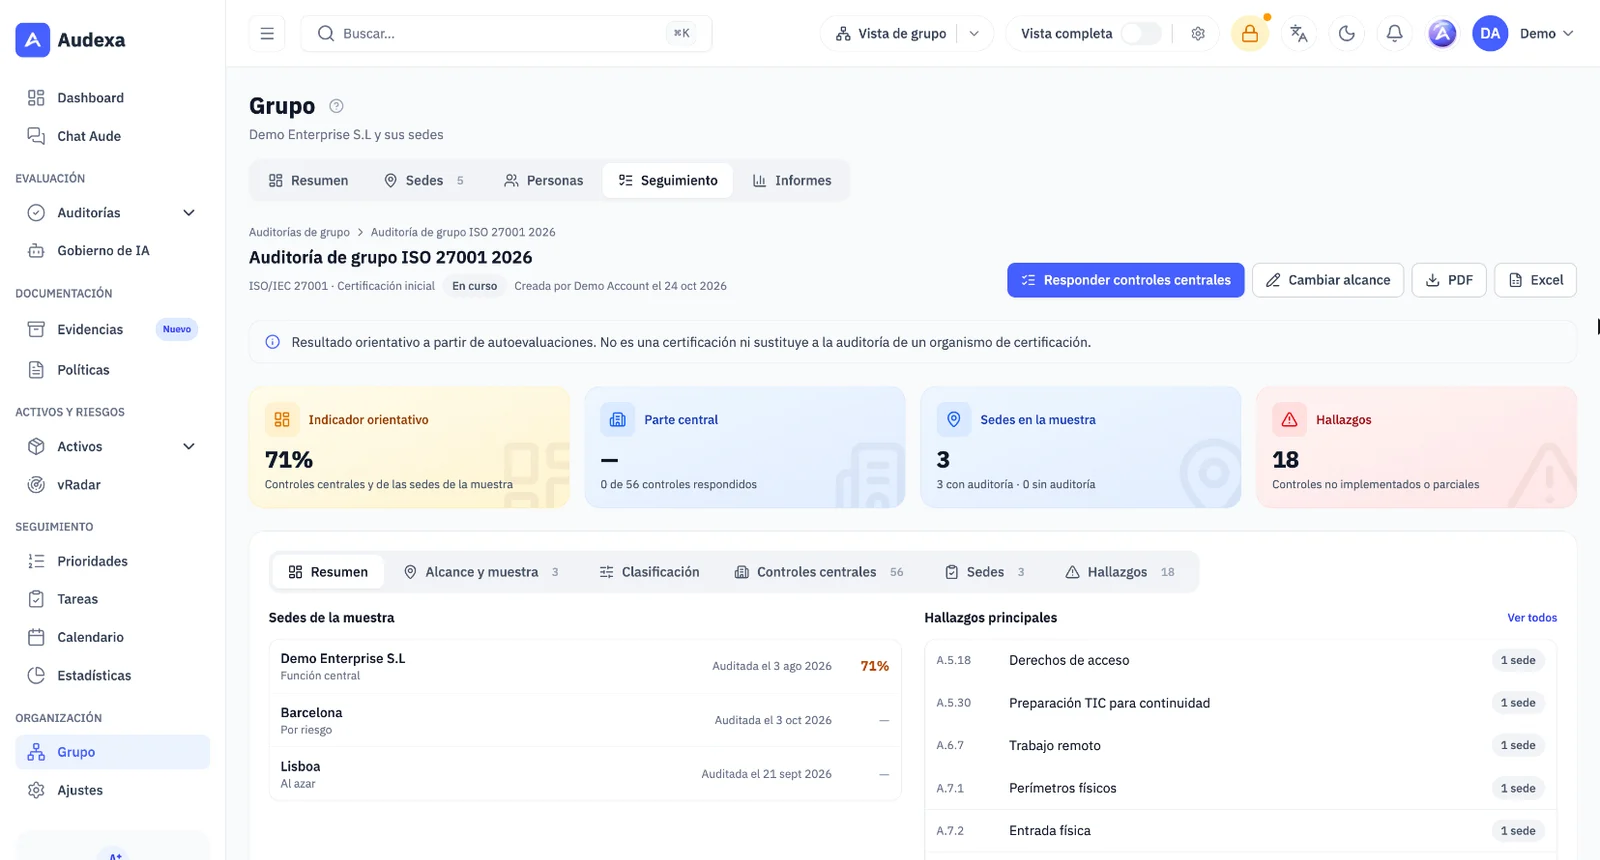
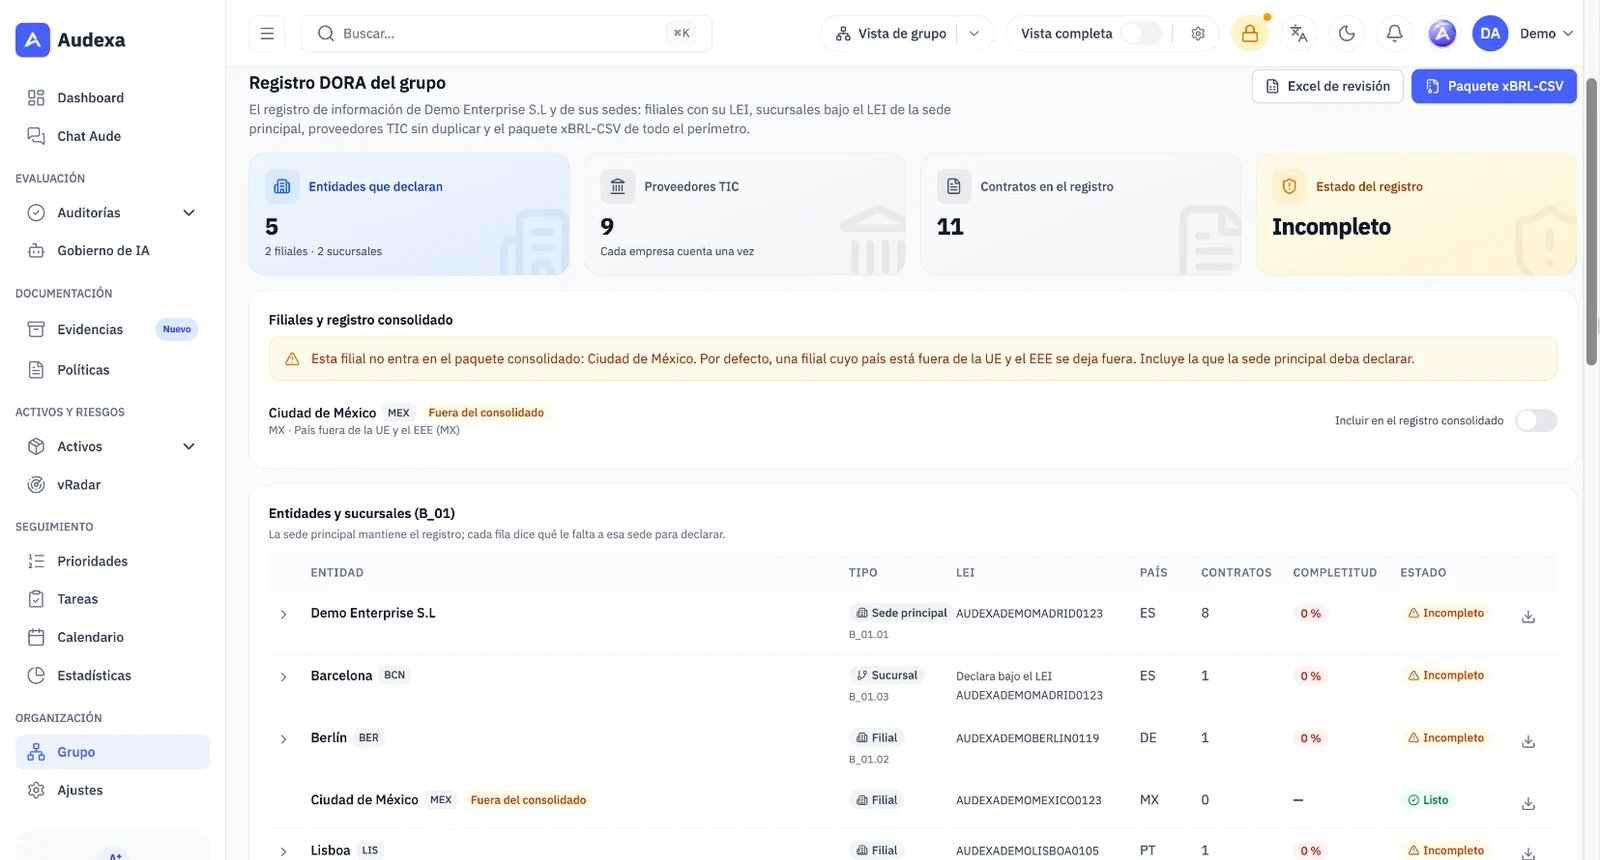
A main site manages its sites, which keep their own data and their own team. You see the group on a map, compare their compliance, assign access by site or region, and prepare the multi-site ISO 27001 audit and the group's DORA register.

  • Group overview with a map, ranking and site comparison
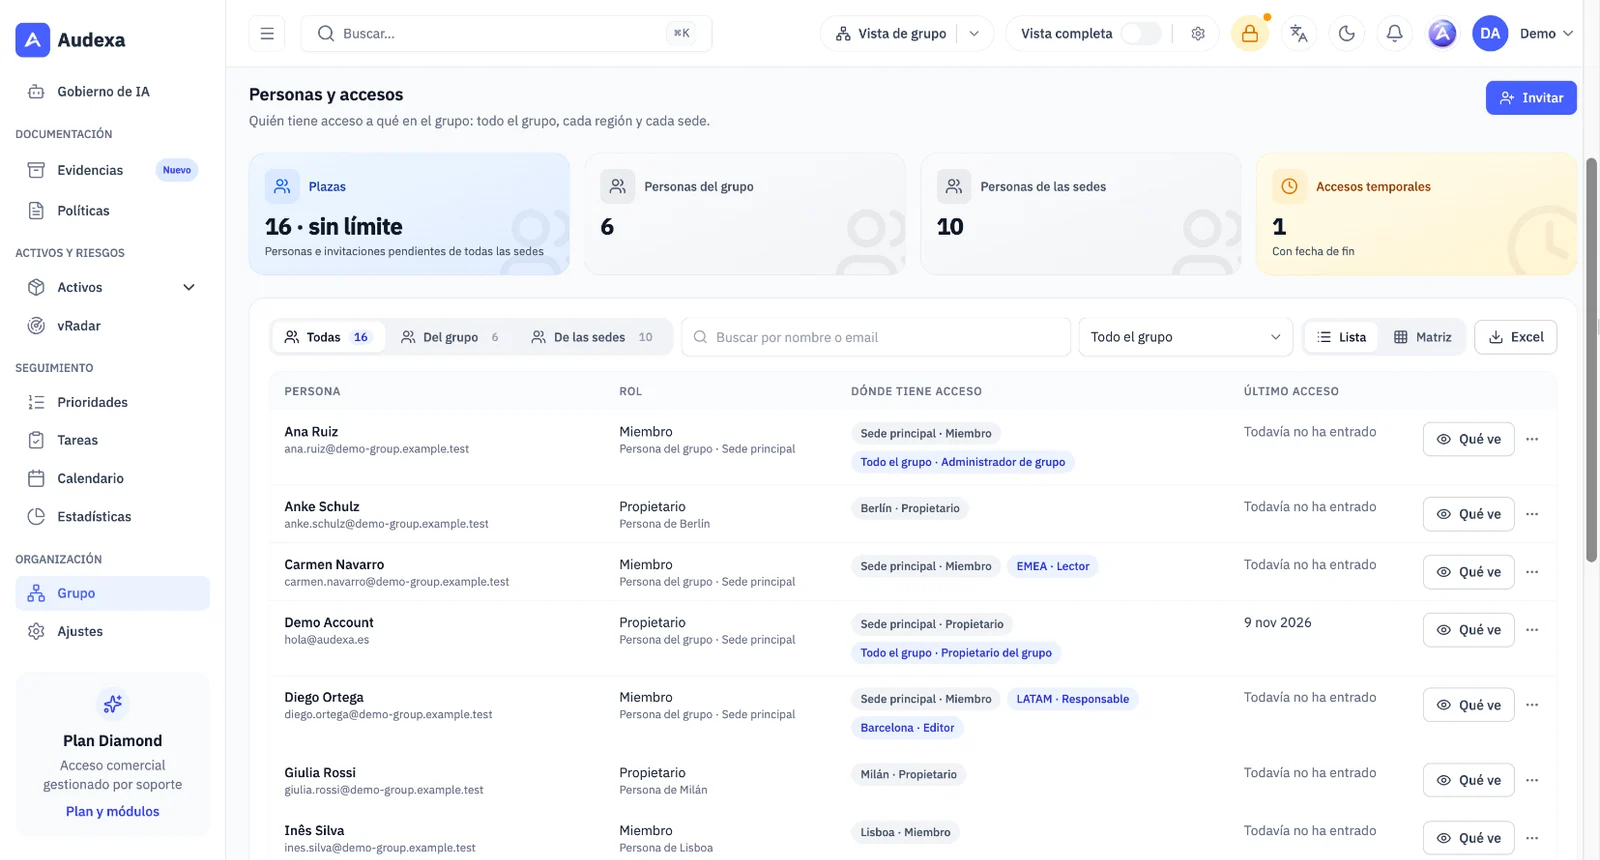
  • Custom roles by group, region or site, and expiring access
  • Suppliers, policies and evidence shared without duplicating work
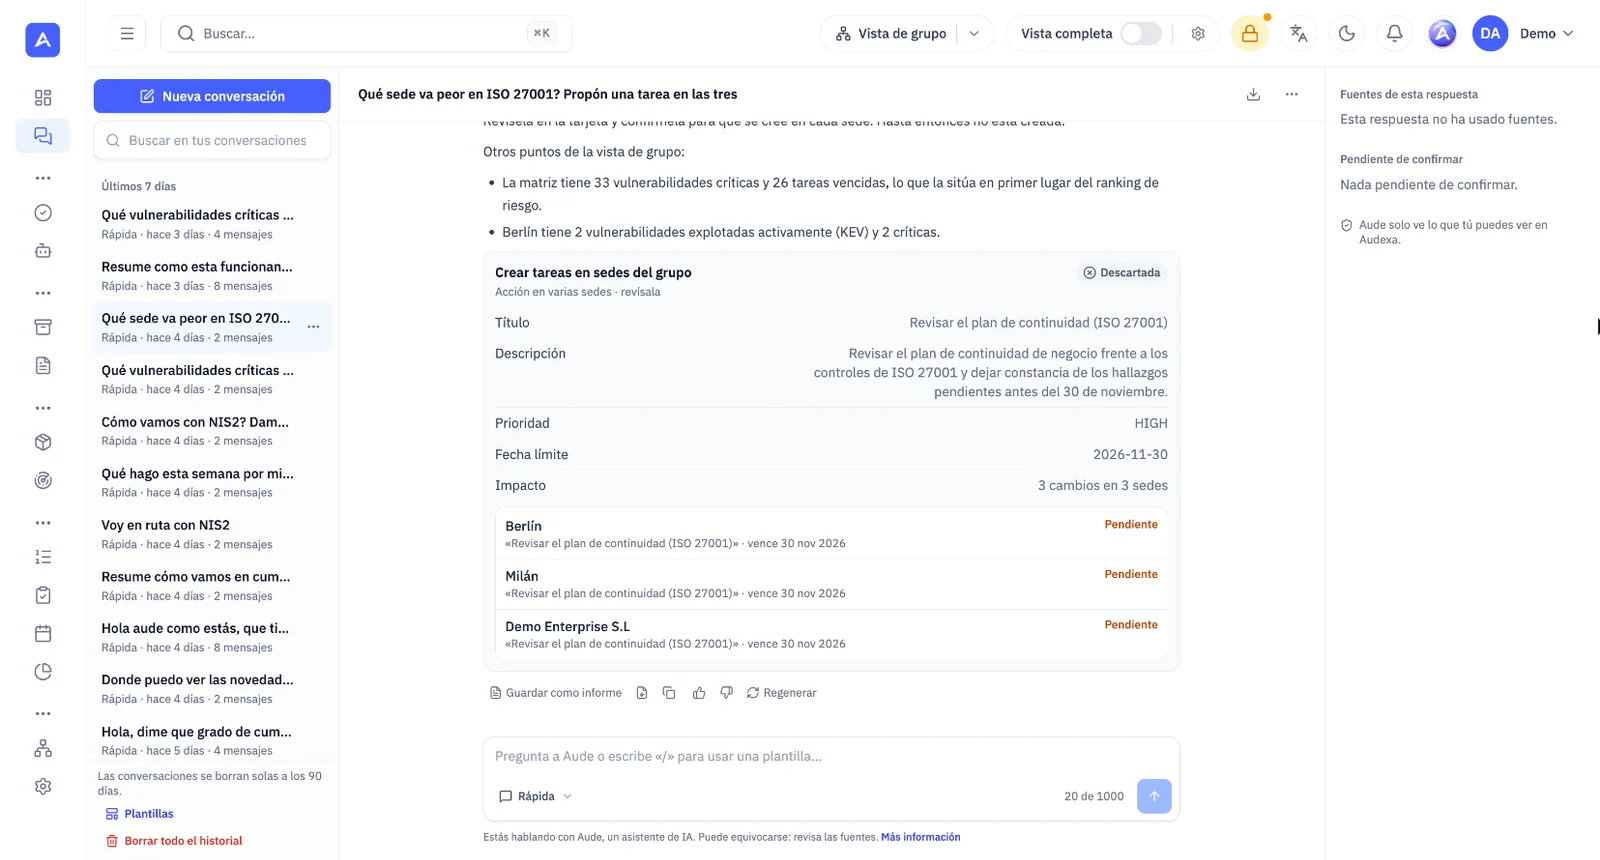
  • Aude answers about the whole group and proposes changes that you confirm

Premium includes 3 sites and Diamond 5, extendable. Audexa activates it on request.

Discover Sites and group
Group overview in Audexa with the map of Europe, the status of each site and the table to compare sites
The status of each site on a map, with the table to compare them.

Also new in 1.7

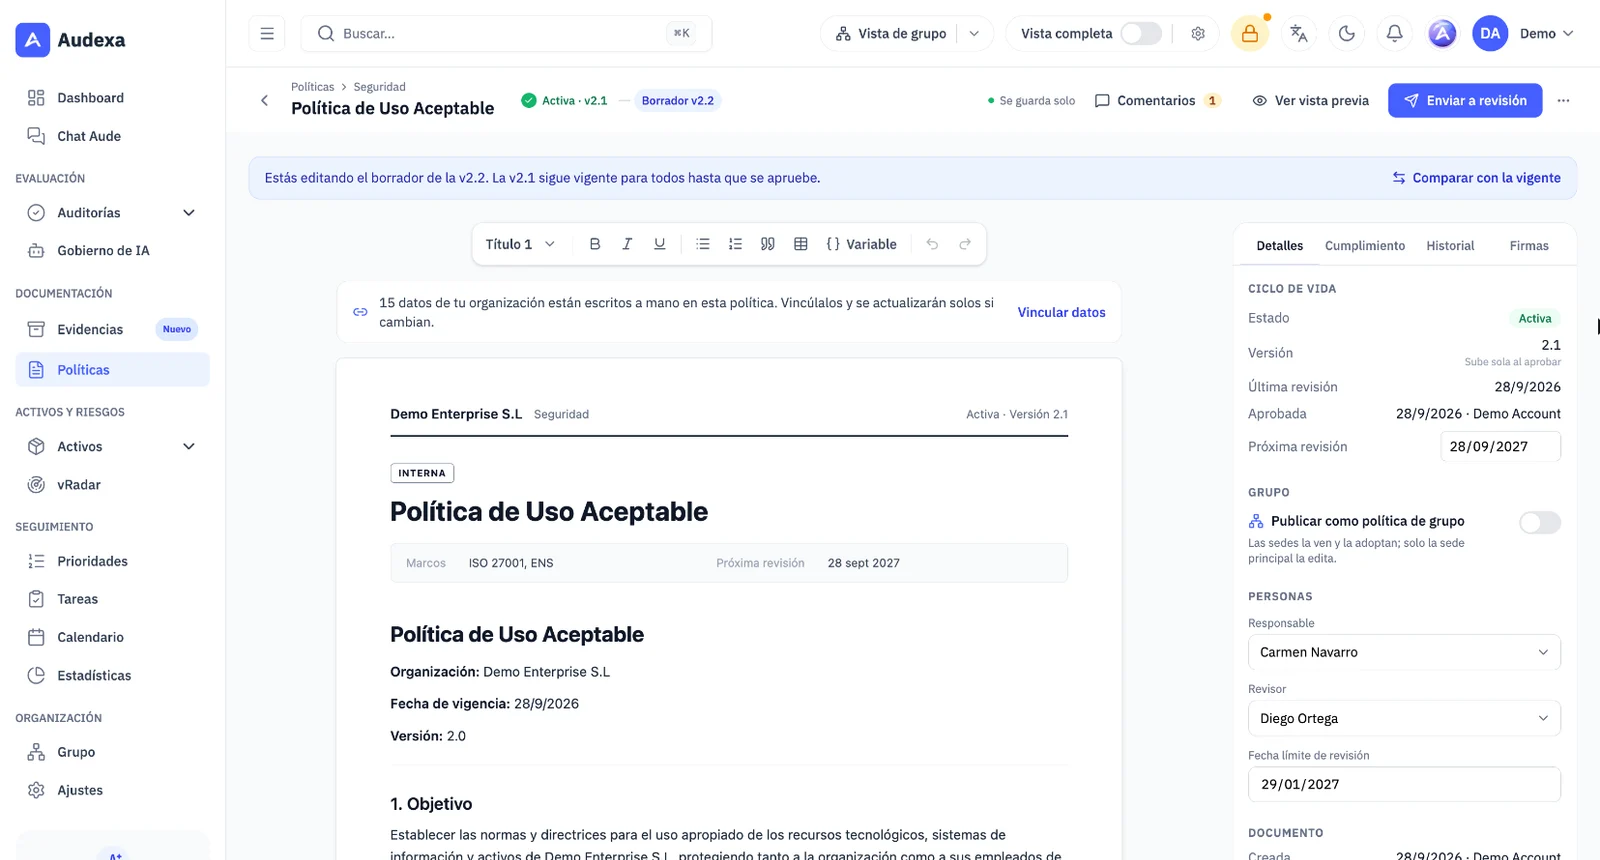
  • Policy editor Versions with drafts, comments in the text, live variables and team reading.
  • Hand over to the auditor Package by control with a SHA-256 fingerprint and a read-only link that expires.
  • vRadar deadlines Days to fix by severity, alerts for what's new and exceptions that expire.
  • Your AI key Aude with your Anthropic, OpenAI or Mistral account, without using your Audexa allowance.
All the 1.7 updates

How it works

From the first audit to the evidence, in one flow.

What lives today in spreadsheets, emails and shared folders becomes one flow in Audexa, with the same context from start to finish.

  1. 01 · Audit

    Audit with guidance, control by control

    Choose your framework and Audexa shows you only what it asks for. Every question comes with its exact reference and suggested answers with their source, which you accept or change, plus a consistency check before submitting.

  2. 02 · Detect

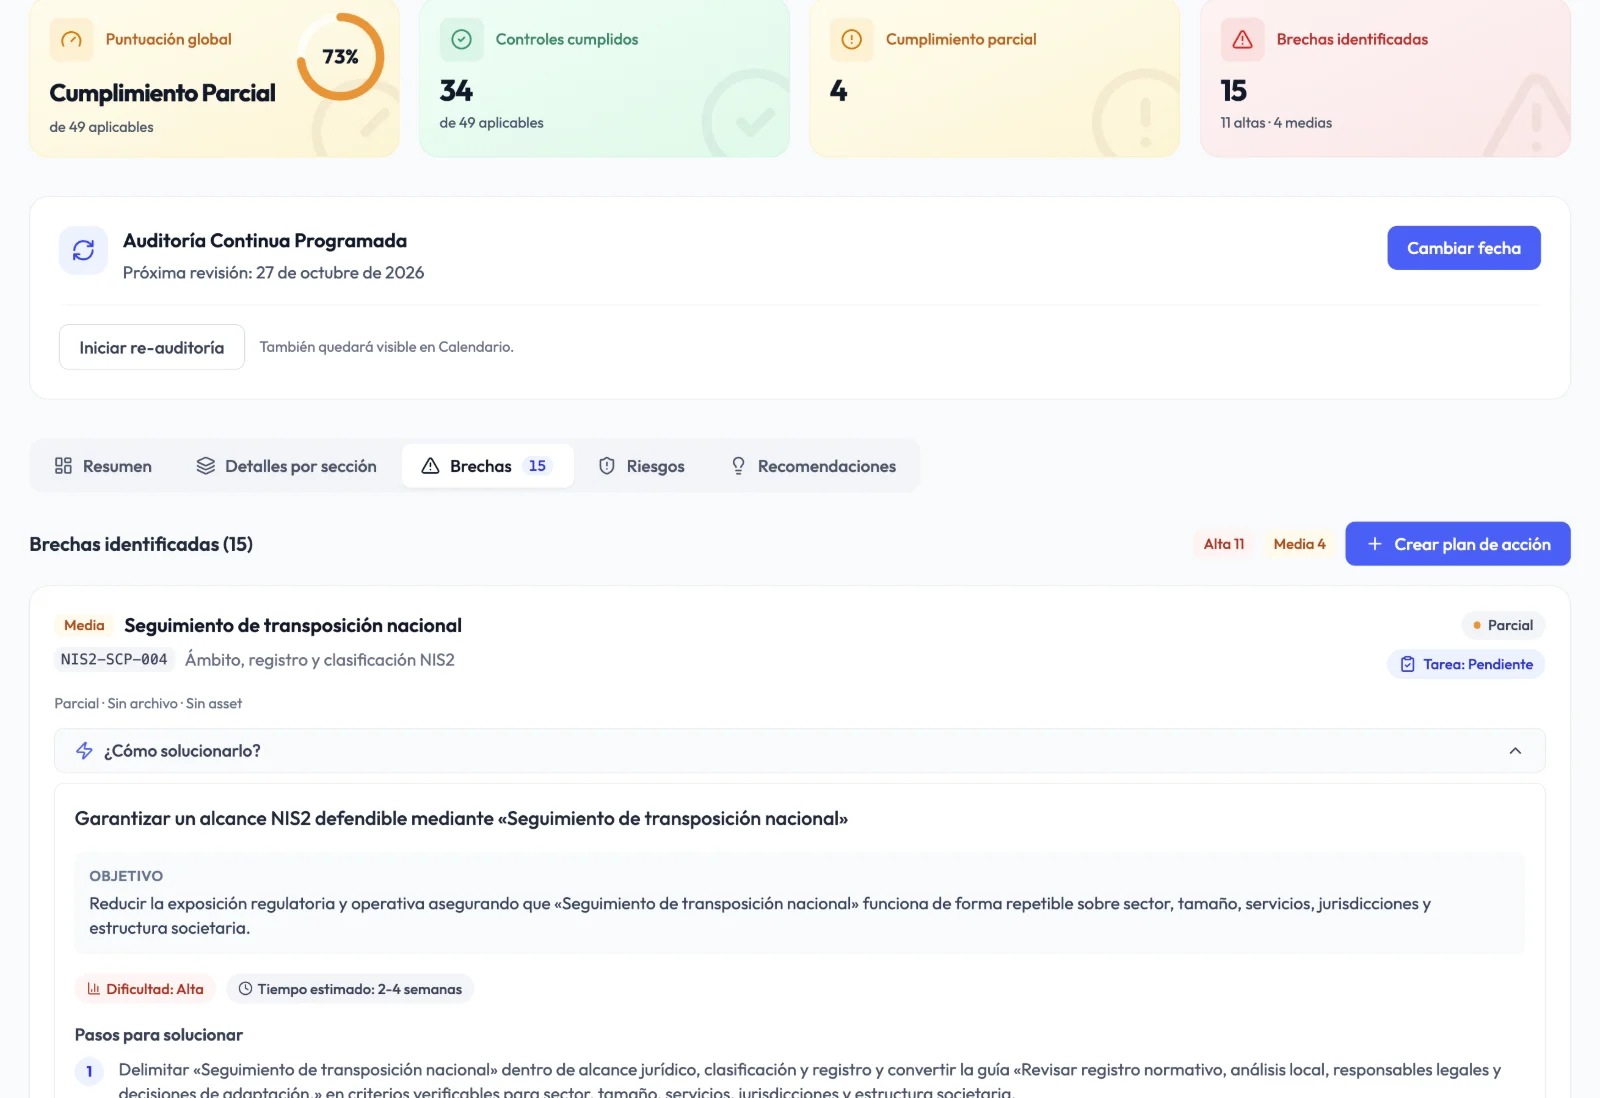
    Spot gaps and risks

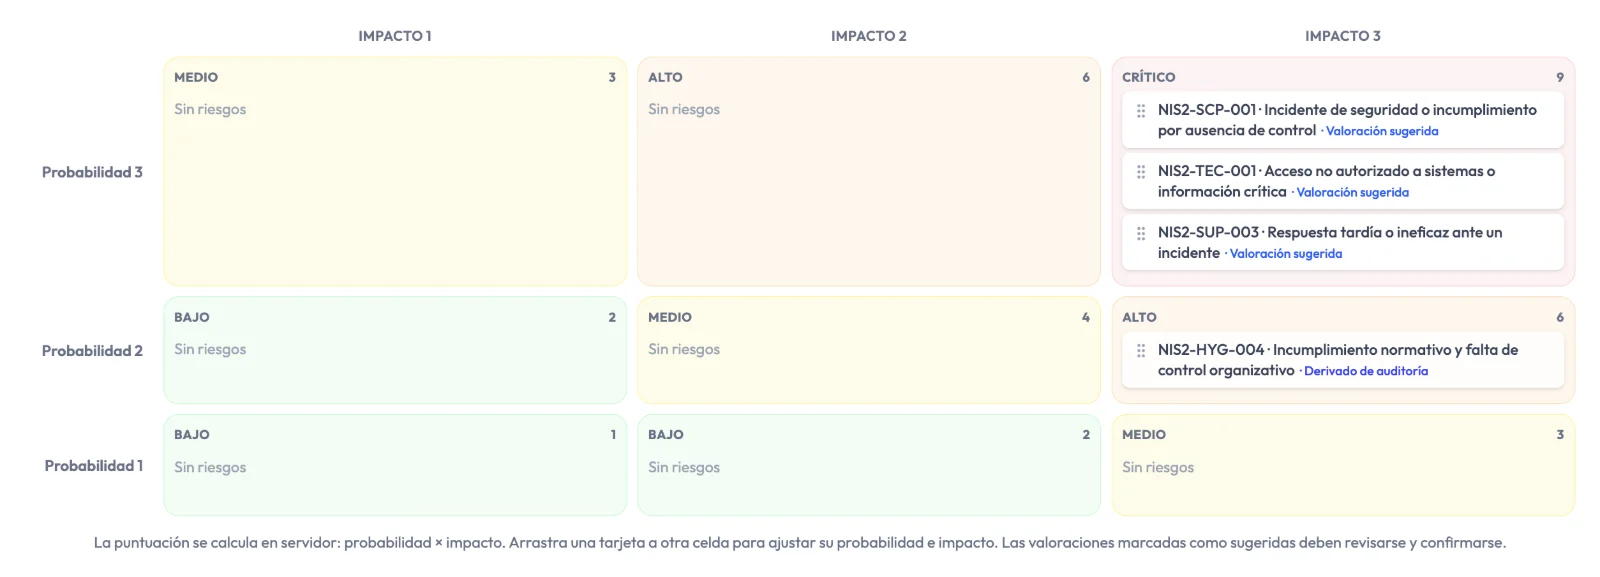
    Gaps are ranked by severity and turned into risks with likelihood and impact, ready for management to decide how to treat them.

  3. 03 · Remediate

    Remediate with an owner

    Each gap becomes a task with an owner, recommended steps and the evidence expected.

  4. 04 · Report

    Prove it to whoever asks

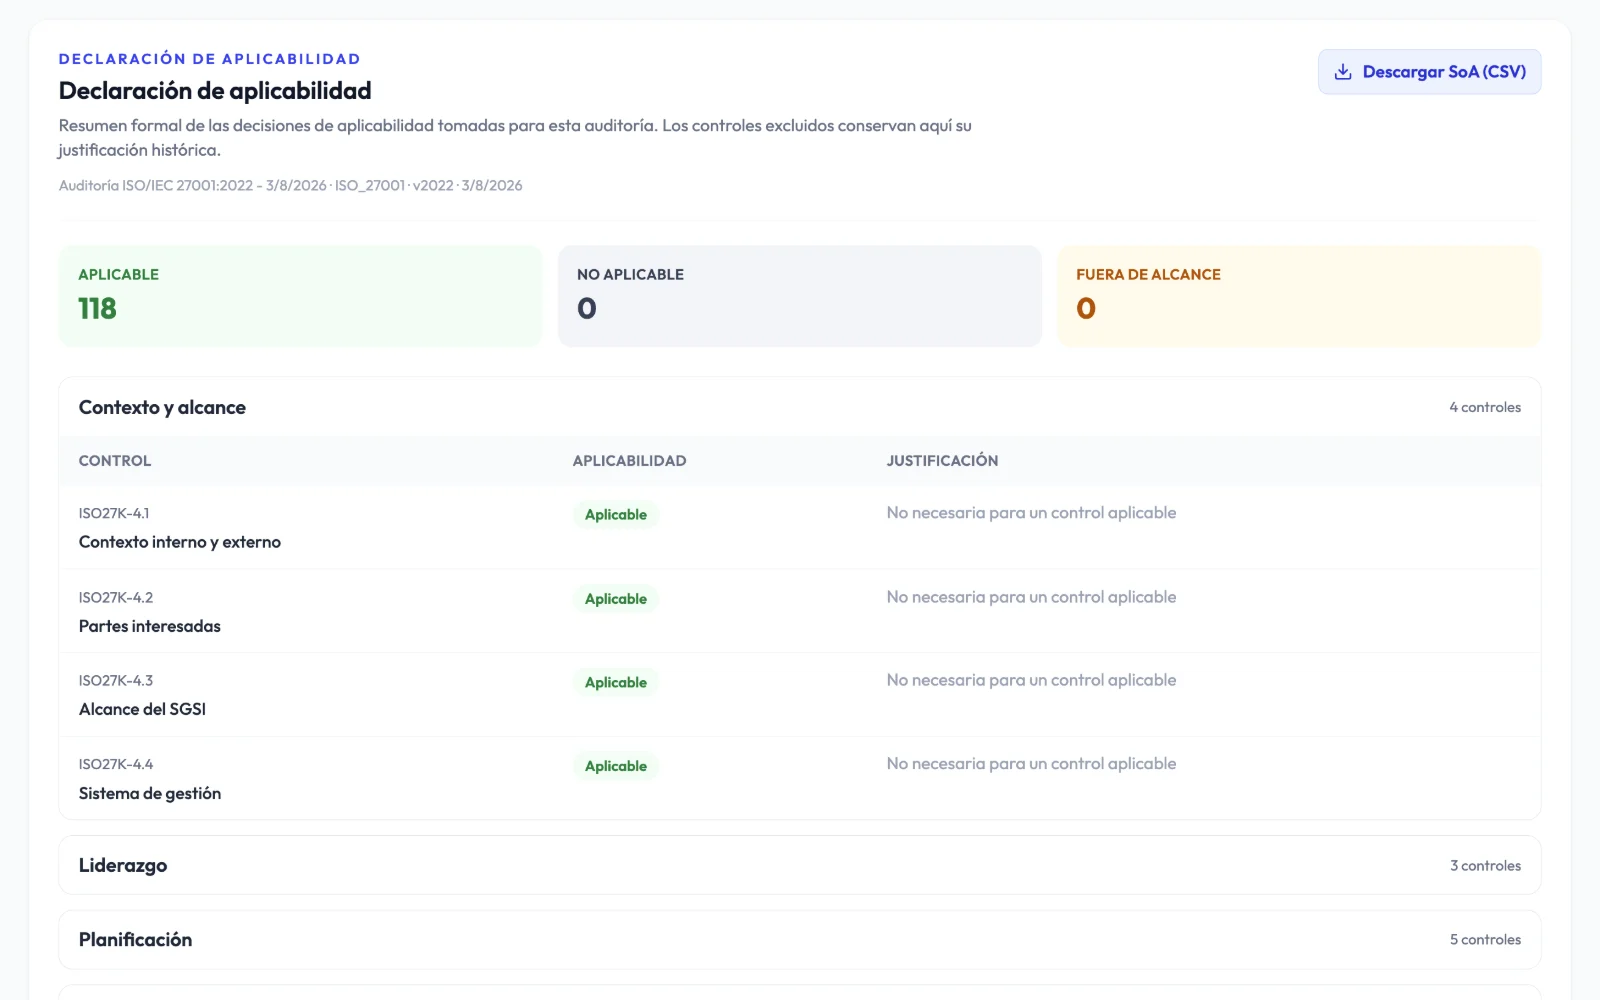
    Statement of applicability, reports for management and an auditor package with an index and a SHA-256 fingerprint for each piece of evidence, or a read-only link that expires.

Platform

Everything your compliance programme runs on, in one place.

Policies, risks, assets, evidence and AI governance connected to your audits, so work is never repeated across frameworks or sites.

Policies and Signatures

Editor with versions, comments, live variables, signatures and team reading, built on 67 templates with framework coverage.

Learn more

Risk Treatment

Risks derived from gaps on a likelihood x impact matrix, with signed management approval.

Learn more

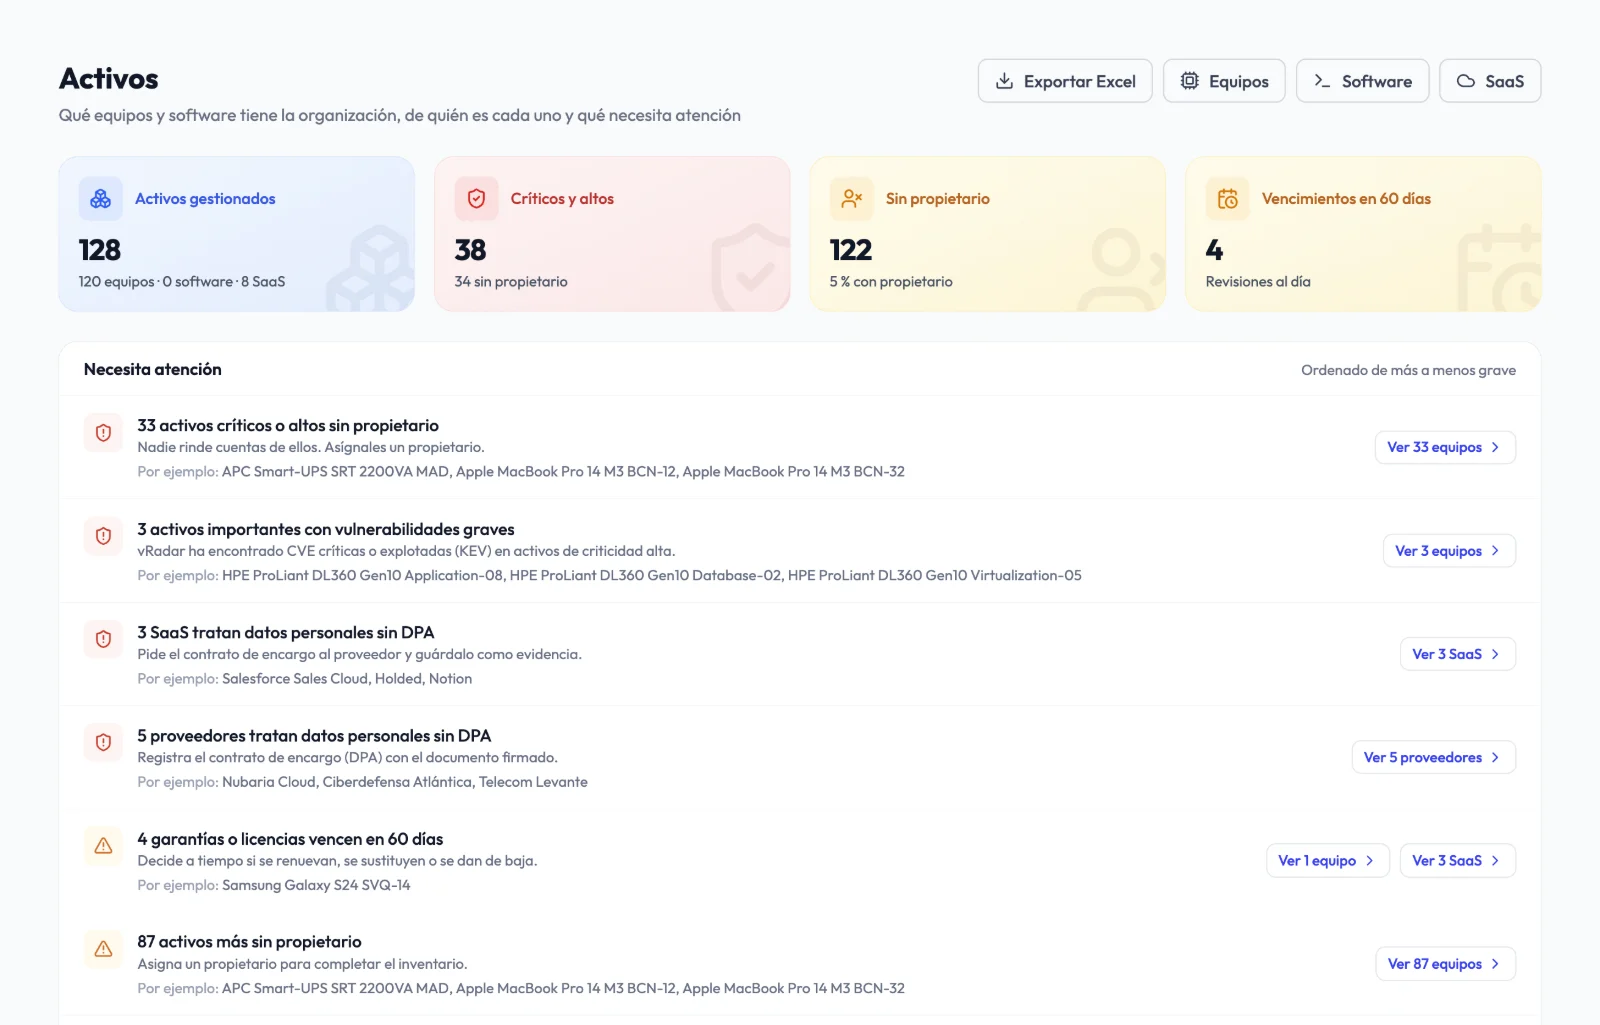
Asset Inventory

Devices, software, SaaS, suppliers and contracts with owners, periodic reviews and renewal alerts.

Learn more

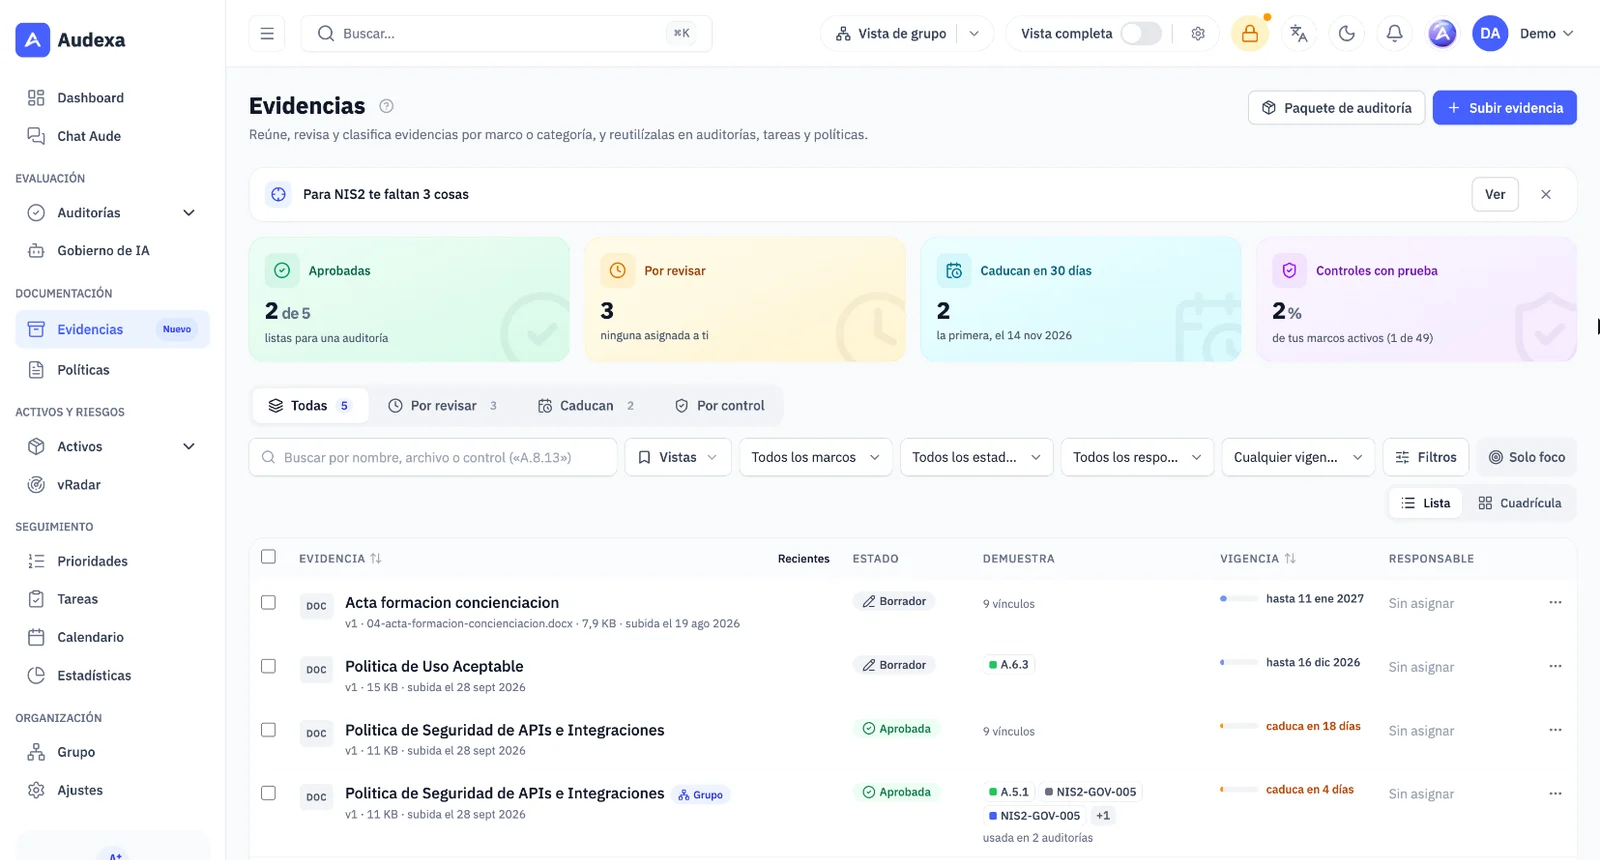
Evidence Vault

Which controls each piece of evidence proves, how long it is valid and who owns it, with handover to the auditor and a SHA-256 fingerprint for each file.

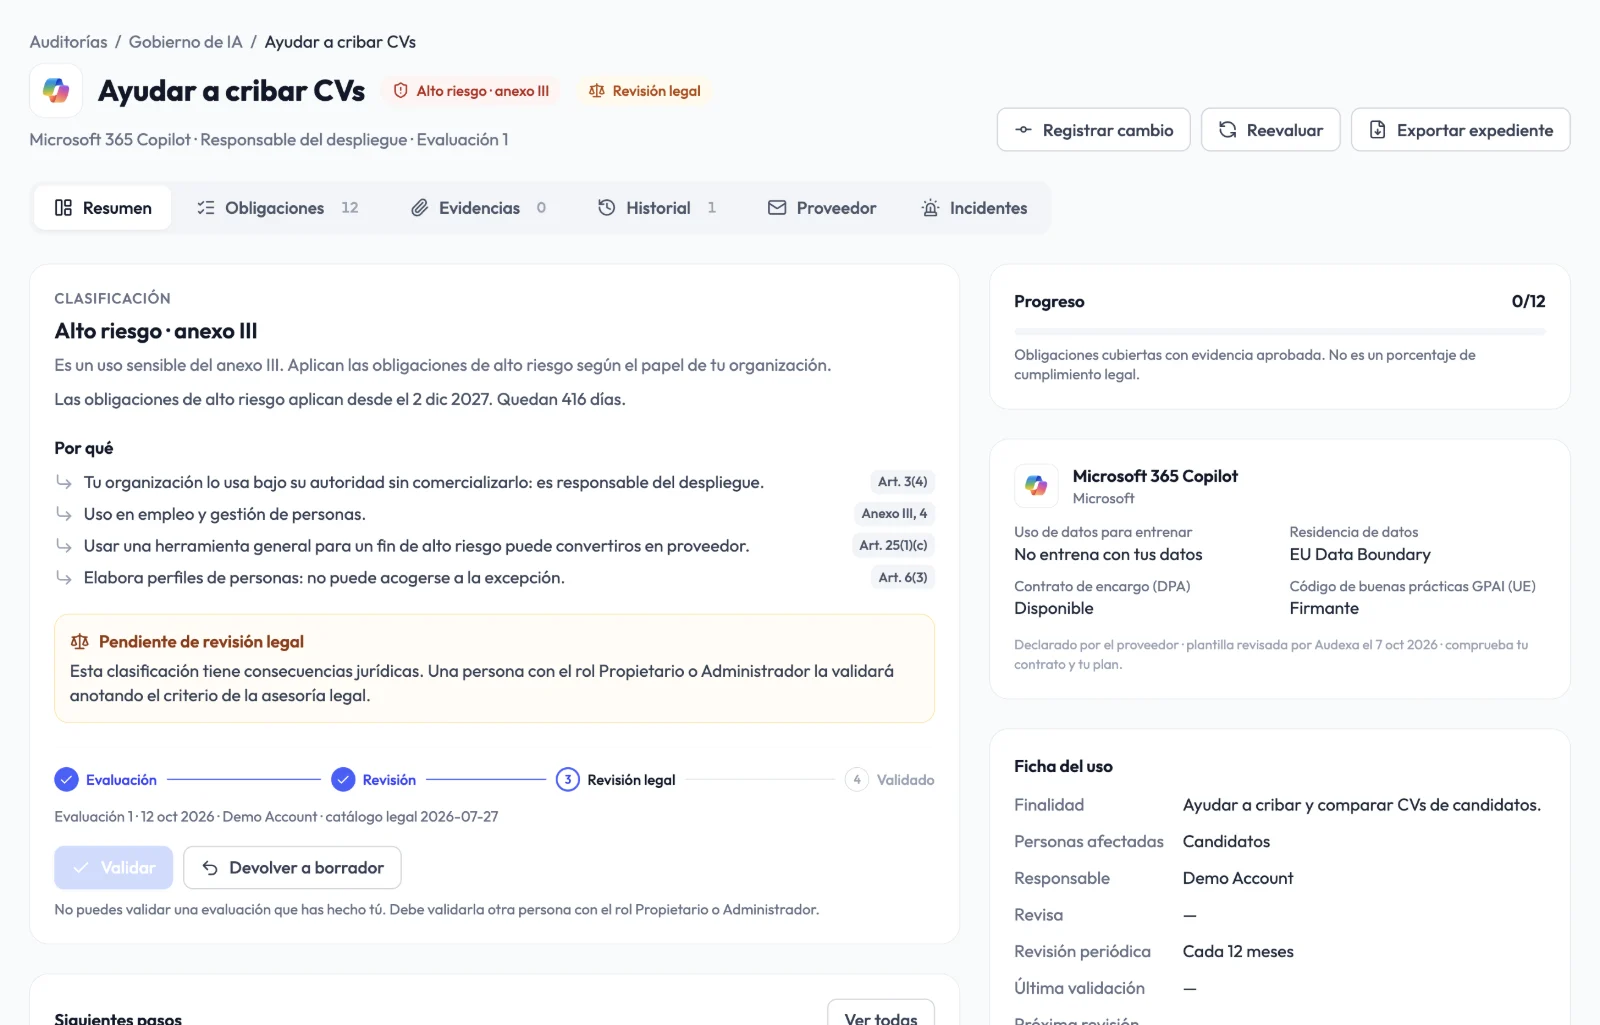
AI Governance

Register AI uses, classify them under the EU AI Act and track obligations with evidence.

Learn more

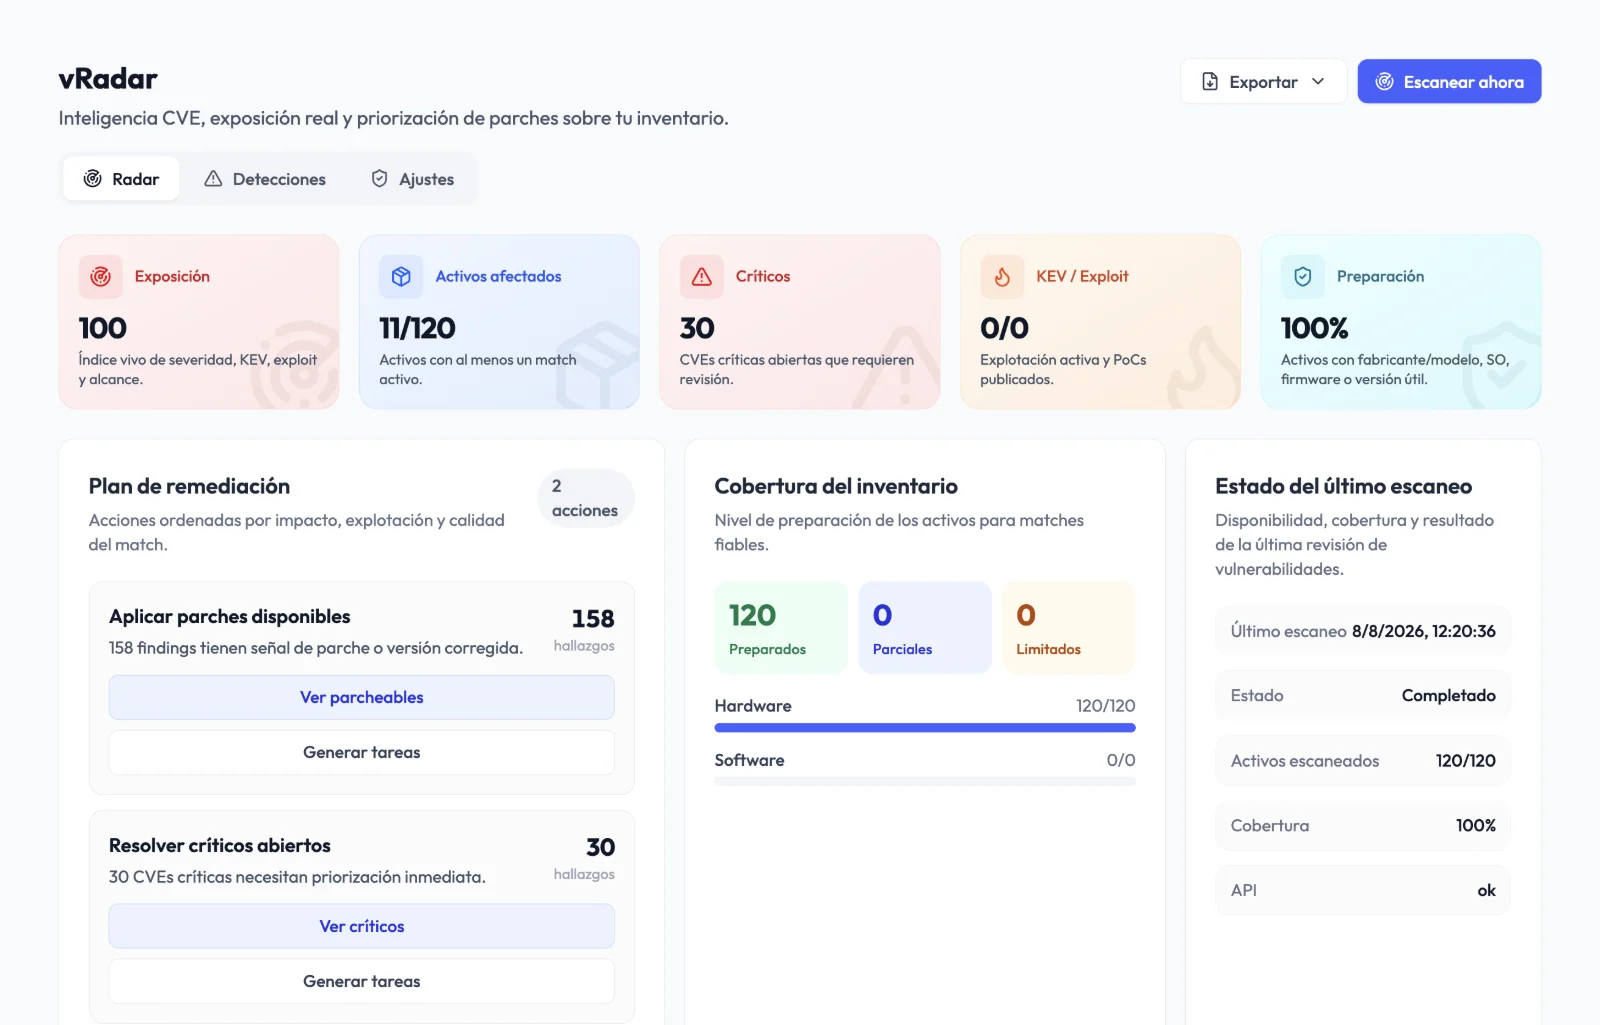
vRadar CVE Intelligence

Prioritize real exposure with CVE, CVSS, EPSS, KEV and asset signals, with remediation deadlines by severity.

And also

  • Focus Mode and Your Path Audexa shows you only what your framework asks for and gives you a single next step, with goals and milestones from Premium.
  • Findings-to-Remediation Create tasks from gaps or CVE findings with risk, owner, steps and expected evidence.
  • Executive + Technical Reports Board summaries and technical packages in PDF, Excel and Word, in 5 languages.
  • Sites and Group Several sites or subsidiaries with their own data, a group overview, custom roles and shared resources. On request, on Premium and Diamond.

Frameworks

22 frameworks with expert content, connected to each other.

Every control includes interpretation guidance, suggested evidence and remediation steps. Thanks to the mappings, what you prove for one framework is reused in the related ones.

Cross-framework mapping

22 frameworks 1,763 controls 2,543 mappings

61 122 43 130 53 48 68 60 78 61 121 80 58 72 135 57 49 46 54 42 77 44 58 54 43 92 70 63 113 35 56 61 85 43 111 48 52 ISO 27001 118 controls ENS 175 controls NIS2 49 controls GDPR 52 controls ISO 42001 94 controls ISO 14001 56 controls ISO 9001 83 controls ISO 22301 77 controls SOC 2 61 controls NIST CSF 2.0 106 controls DORA 81 controls CRA 67 controls ISO 27017 64 controls ISO 27018 129 controls ISO 27701 73 controls LOPDGDD and LSSI 48 controls EU AI Act 93 controls ISO 45001 65 controls ISO 20000-1 75 controls ISO 37301 / UNE 19601 68 controls Whistleblowing 61 controls TPRM 68 controls

Hover or tap a framework · Numbers show related control pairs

  • ISO 27001 – NIS2: 61
  • ISO 27001 – ENS: 122
  • ISO 27001 – GDPR: 43
  • ISO 27001 – NIST CSF 2.0: 130
  • ISO 27001 – ISO 9001: 53
  • ISO 27001 – ISO 14001: 48
  • ISO 27001 – DORA: 68
  • ISO 27001 – TPRM: 60
  • ISO 27001 – ISO 42001: 78
  • ISO 27001 – ISO 22301: 61
  • ISO 27001 – ISO 27018: 121
  • ISO 27001 – ISO 27017: 80
  • ISO 27001 – ISO 27701: 58
  • ISO 27001 – ISO 20000-1: 72
  • ISO 27001 – SOC 2: 135
  • ISO 27001 – CRA: 57
  • ISO 14001 – ISO 9001: 49
  • DORA – ISO 22301: 46
  • DORA – NIS2: 54
  • DORA – TPRM: 42
  • NIS2 – ENS: 77
  • NIS2 – CRA: 44
  • ISO 42001 – ISO 9001: 58
  • ISO 27018 – GDPR: 54
  • ISO 27017 – ISO 27018: 43
  • ISO 27701 – GDPR: 92
  • ISO 27701 – ISO 27018: 70
  • LOPDGDD and LSSI – GDPR: 63
  • EU AI Act – ISO 42001: 113
  • EU AI Act – GDPR: 35
  • ISO 45001 – ISO 9001: 56
  • ISO 45001 – ISO 14001: 61
  • ISO 20000-1 – ISO 9001: 85
  • ISO 20000-1 – ISO 22301: 43
  • SOC 2 – NIST CSF 2.0: 111
  • ISO 37301 / UNE 19601 – Whistleblowing: 48
  • ISO 37301 / UNE 19601 – ISO 9001: 52

Management systems

  • ISO 9001 83 controls
  • ISO 14001 56 controls
  • ISO 45001 65 controls
  • ISO 20000-1 75 controls
  • ISO 22301 77 controls

Personalized Journey

Different roles, one compliance execution layer.

Ship compliance without creating a new department

Current friction: You need visibility, budget control and predictable execution without adding consulting overhead.

With Audexa: Audexa centralizes frameworks, risks, reports and remediation in one operating layer.

What changes

One dashboard for every framework, risk and deadline

What improves in the first 30 days

  • Consolidated controls and owners in one board
  • Weekly executive snapshot without manual slides
  • Predictable roadmap across NIS2, ENS, ISO and vulnerability risk

Cost and control

What changes compared with relying on a consultancy.

Area Traditional consulting With Audexa
Time to first audit Weeks of interviews and preparation Same day
Cost predictability Variable consulting scope Tiered plans with a fixed proposal
Work across frameworks Every framework starts from scratch 2,543 mappings to reuse evidence
Vulnerability visibility Separate scanners and spreadsheets Inventory-linked CVE intelligence
Policy lifecycle Static documents Templates, variables, versions and signatures
Programme knowledge Leaves when the project ends Stays in your platform, with history
Several sites or subsidiaries One Excel file per site Group overview and shared resources

Plans

Choose the right starting point for your compliance program.

Free

Try Audexa with one free ISO 27001 audit.

  • 1 free ISO 27001 audit
  • Platform access
  • 1 executive report (PDF)
  • Audit tasks
  • Focused view and Your path
Start for free

Core

For teams starting with the essential compliance workflows.

  • 5 audits / month
  • NIS2, ISO 27001 and ENS
  • Technical reports (PDF / Excel)
  • Statement of applicability and statistics
  • Risk matrix and accepted-risk dossier
  • 20 assets per section
  • 1 user
Request a demo

Diamond

For organizations that need the full compliance operating layer.

  • Unlimited audits · all 22 frameworks
  • Everything in Premium
  • vRadar CVE exposure intelligence
  • Unlimited assets and users
  • More Aude and API capacity
  • Your own AI key included
  • Mandatory 2FA
Request a demo
See the full plan comparison

Security and integrations

Connects to your tools and protects your information.

Audexa integrates with the tools you already use and applies access and file controls designed for sensitive information.

Integrations

  • Microsoft Entra ID

    Single sign-on (SSO) with your corporate account.

  • NinjaOne

    Syncs devices and software with the asset inventory.

  • SentinelOne

    Brings the endpoints your agents protect into the inventory.

  • Jira Cloud

    Creates Jira issues from remediation tasks (Premium and Diamond).

  • API and MCP

    Connect your tools and AI assistants, with the permissions you set on each key (Premium and Diamond).

  • Your AI key

    Aude can use your Anthropic, OpenAI or Mistral account without using your Audexa allowance (Diamond; Premium on request).

Platform security

  • Two-factor authentication

    By email or authenticator app. Mandatory on Diamond.

  • Roles and permissions

    Everyone works with a role: owner, admin, editor, viewer or member. In a group, custom roles by site or region.

  • Expiring access

    Give an external auditor access with an end date: Audexa warns you 7 days before and removes it automatically.

  • Fingerprinted signatures

    Policies and accepted risks are signed with a SHA-256 fingerprint of the approved version.

  • Private files

    Evidence and attachments stay private, with authenticated downloads and blocking of files with obvious malware.

  • Isolated by organisation

    Each organisation works in its own space, and integration credentials are stored encrypted.

  • Data in the European Union

    Databases and backups in Barcelona; evidence and attachments in Paris.

Frequently asked questions

Answers to help you get started with Audexa.

Where is our data hosted and how is it protected?

Audexa runs on EU infrastructure with encrypted data flows and role-based access. Activity history remains traceable for internal and external audit review.

How long does implementation take?

Most teams launch their first guided audit the same day and complete the initial assessment in under 60 minutes.

What support is included after onboarding?

All plans include product support. Expert-led recurring calls and enhanced support are available separately through the Enterprise Support plan.

Can we try Audexa before committing?

Yes. The Free plan includes one ISO 27001 audit, one executive PDF report and platform access so you can validate fit before scaling.

Is there a long-term commitment?

It depends on the contract and the agreement reached in each case. Longer commitments can come with attractive discounts; we agree the terms with you before you subscribe.

Does Audexa issue official certificates?

No. Audexa gets you ready: with “Hand over to the auditor” you check what is missing and download a package organised by control with an index and a SHA-256 fingerprint for each file, and the “Would you pass an external audit today?” review is guidance, never a verdict. Official certificates are issued by accredited external auditors.

What is vRadar?

vRadar is Audexa's CVE intelligence module. It connects hardware and software inventory with CVSS, EPSS, KEV and public exploit signals so teams can prioritize real exposure and create remediation tasks. You set remediation deadlines by severity and vRadar alerts you to anything overdue.

Does Audexa work for consultancies?

Yes. Audexa helps consultancies run their clients' audits with a guided methodology, cross-framework mappings and exports ready for the auditor. If you work with several clients, tell us about your case and we'll suggest how to organise it.

How does Audexa manage policies over time?

They are created from 67 templates and edited on the document exactly as it will be output. Editing an active policy creates the draft of the next version, which is commented on, reviewed and approved; live variables keep your organisation's name or the owner up to date, and your team confirms which version it has read.

Does Audexa answer the audit for me?

No. Audexa suggests answers with their source (evidence, other audits, assets, policies and tasks), flags answers that don't add up and tells you what counts as evidence for each question, but a person accepts or changes each answer and decides when to submit.

Can I manage several sites or subsidiaries?

Yes, with Sites and group. A main site manages branches and subsidiaries that keep their own data and their own team, with a group overview, custom roles by site or region and shared resources. Premium includes 3 sites and Diamond 5, extendable, and Audexa activates it on request.

Can I give an external auditor access?

Yes. You can give them access with an end date, which Audexa removes automatically, or share a read-only link to the evidence package that expires and that you can revoke, with every access visible.

Get Started

Let's talk about your compliance priorities.

Tell us where you want to improve visibility, execution and risk control, and we will help you identify the right starting point.

  • Centralize audits, risks, policies, evidence and assets in one operating layer.
  • Turn findings into clear actions with owners, deadlines and traceability.
  • Give leadership an executive view of progress, risk and next steps.

Fields marked with * are required.

We use these details to respond to your request and manage follow-up. Read our Privacy Policy.

Complete the required fields to send your request.

Short Demo

Guided NIS2 audit walkthrough (1 min)

  • How guided audits adapt to your selected framework
  • How gaps and vRadar findings become remediation tasks
  • How policies, evidence and reports stay versioned