
Context and scope
Define the ISMS scope, the interested parties and the requirements that apply to the organization.
ISO/IEC 27001:2022
Audexa organizes your ISMS in a single workspace: clauses and Annex A assessed control by control, a Statement of Applicability, approved policies, evidence with expiry dates and an action plan to get you to the certification audit.
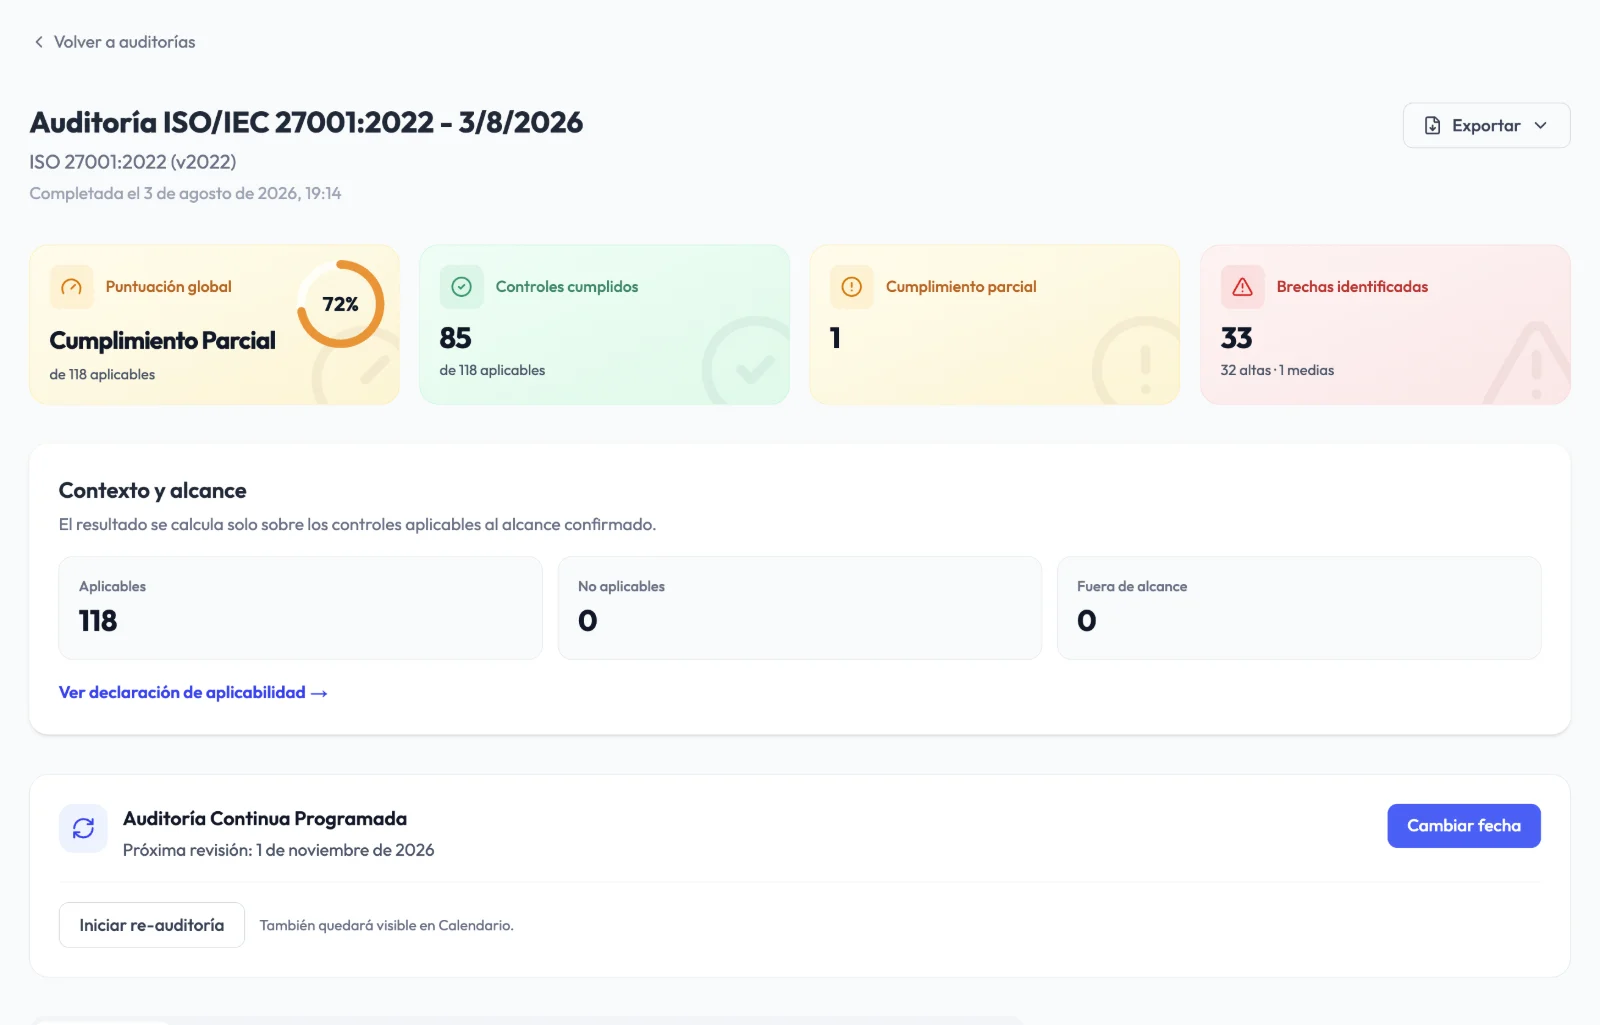
What the standard requires
The 2022 edition reorganized Annex A into 93 controls and four themes. The transition from the 2013 edition ended on October 31, 2025, so valid certificates must now be on the 2022 edition.
Define the ISMS scope, the interested parties and the requirements that apply to the organization.
Top management approves the information security policy, assigns roles and provides resources.
A repeatable risk method and a treatment plan consistent with the selected controls.
Which Annex A controls apply, which don't and why, with their implementation status.
Records, procedures and proof that controls work, not just that they exist.
Internal audit, management review and corrective actions to close the loop.
How Audexa helps
Assess, decide applicability, carry out remediation and keep the evidence without relying on shared folders.
Know the status of every clause and control.
Clauses 4 to 10 and Annex A grouped by theme, with guidance, weighting, remediation steps and the clause or control behind each question.
With ISO 27001 as your focus, Audexa shows you only what the standard asks for and a single next step. One framework, on every plan.
Suggested answers with their source in your first audit, a consistency check before submitting (it warns, never blocks), points per gap and questions shared out across the team.
Repeat the audit with the same scope and compare progress between cycles.
Answers with high coverage are suggested as reviewable drafts in NIS2, ENS or GDPR.
Decisions and work with full traceability.
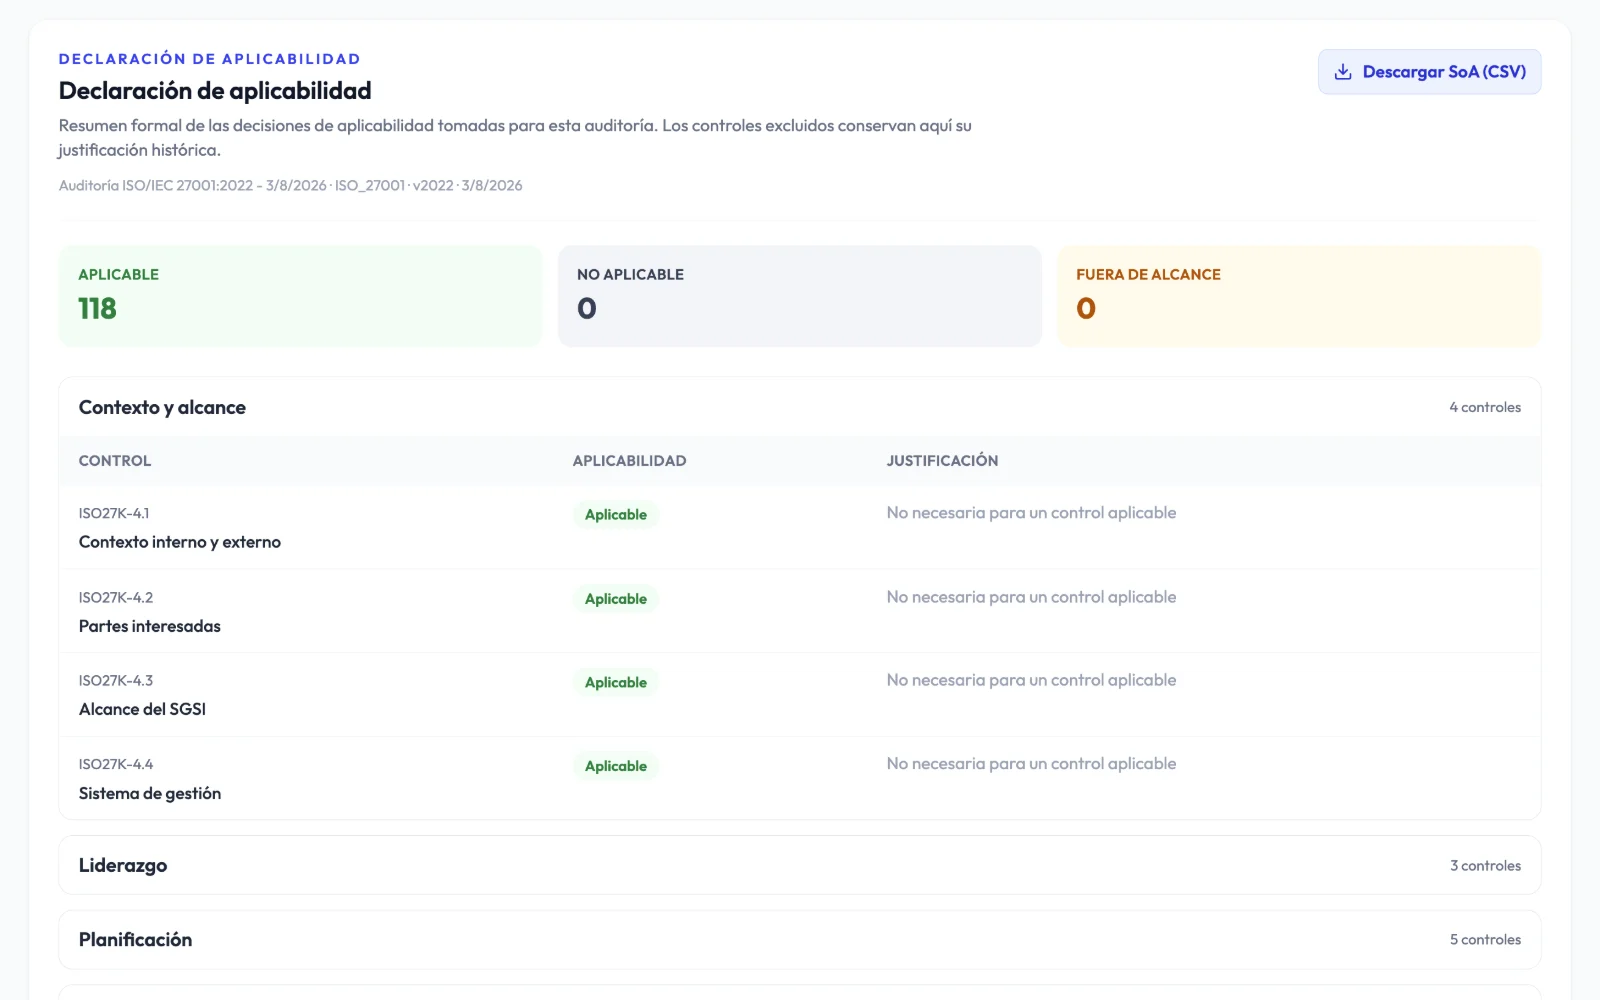
Mark controls as applicable, not applicable or out of scope with a justification, and export them.
Likelihood and impact matrix, treatment and risk acceptance signed by management.
Devices, software, SaaS and suppliers with an owner and periodic review.
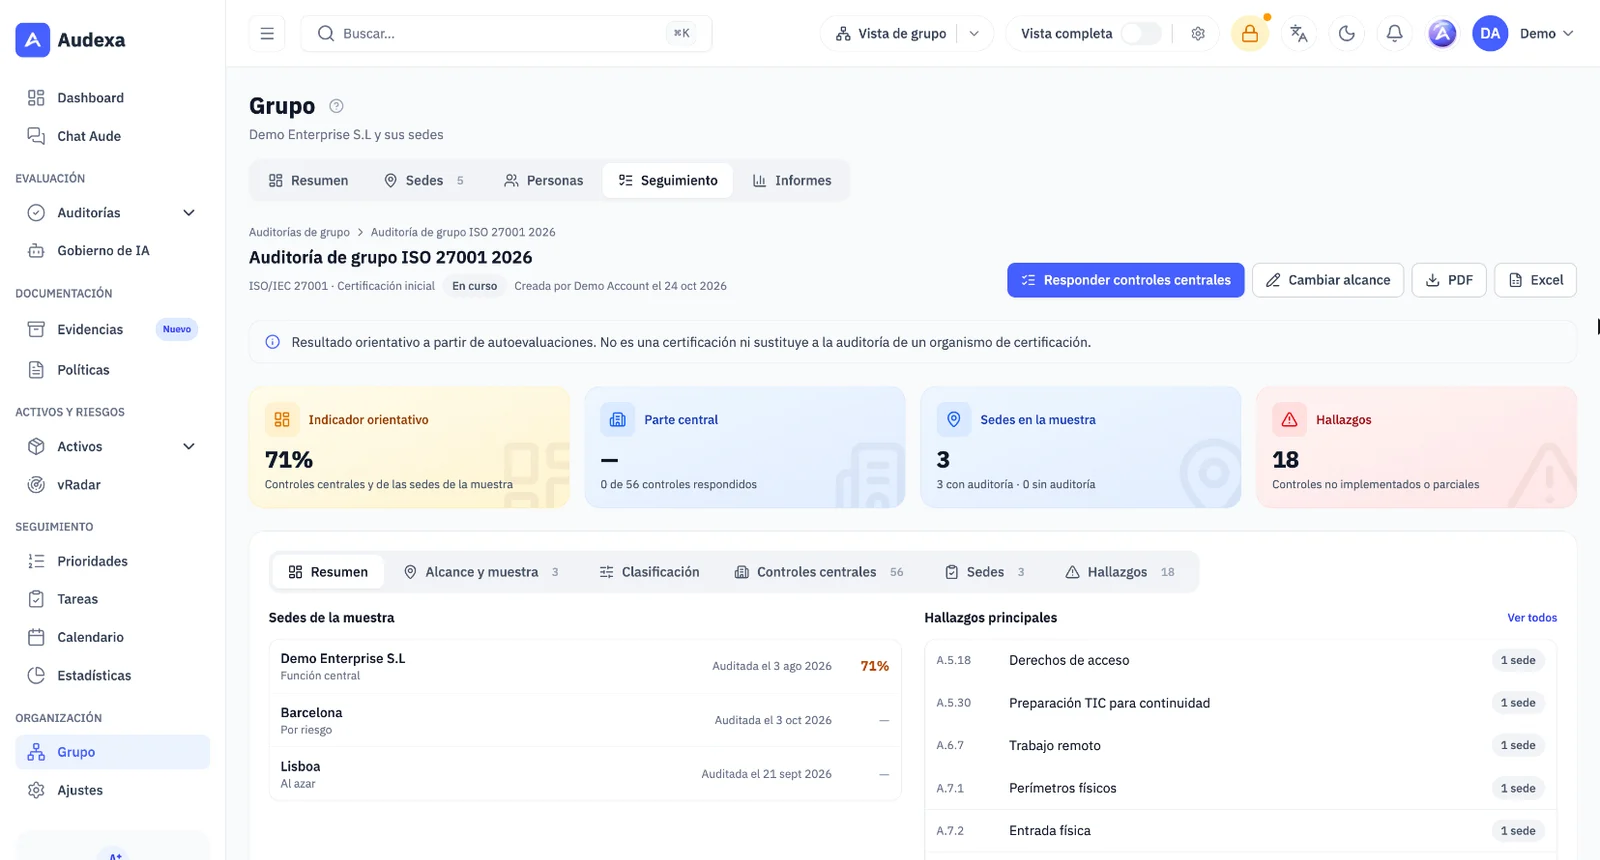
With Sites and group, central controls are answered once at the main site and each site's controls come from its latest audit. Audexa proposes a sample by phase and risk; your certification body confirms the final one.
Organized evidence for auditors.
43 templates linked to ISO 27001 with versions, approval and signature.
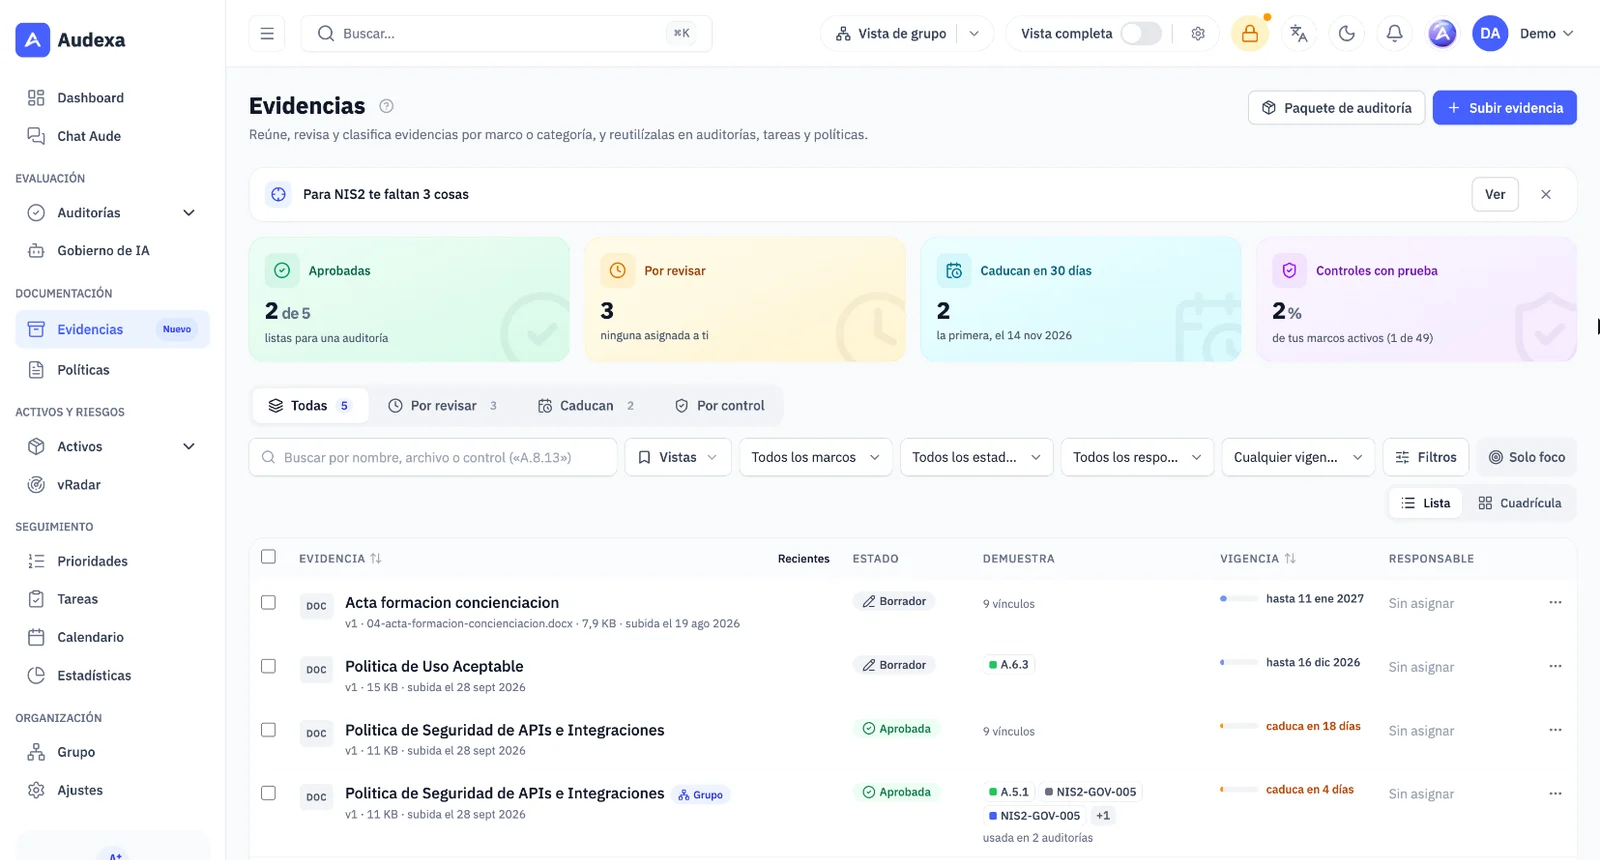
Documents with an owner, review, expiry and history, linked to each control.
Check what is missing and download a package organized by control with an index and SHA-256 fingerprint, or share a read-only link that expires and that you can revoke.
Some features depend on your plan and active modules.
Statement of Applicability
Before answering, decide which controls apply. Every exclusion keeps its justification, and the statement is exported with the organization's context and the applicability of each control.
Evidence
Upload a document once and link it to controls, tasks, policies or risks. Audexa tracks its expiry and review so you never present out-of-date proof.
Before certification
From Premium, Audexa reviews your controls and marks each one as Ready, Needs evidence or Needs work, with a sample explained in one line and a Rehearsal with Aude. It is guidance only, never a verdict: your certification body decides.
Several sites
With Sites and group, central controls are answered once at the main site, and site controls are read from each site's latest completed ISO 27001 audit. Audexa proposes a sample of sites based on each one's phase and risk, and you can change it.
How it works
Assess the clauses and Annex A and get your score, your gaps and an executive report.
Turn gaps into tasks, approve policies and link evidence to each control.
Re-audit, check whether you would pass an external audit today and hand the evidence package to your auditor.
Before and after
Statement of Applicability
Excel disconnected from reality
Generated from the audit itself
Evidence
Folders with questionable versions
Vault with expiry, review and history
Policies
Word files without version control
Templates with approval and signature
Follow-up
Gaps in a static report
Tasks with owners and re-audits
Other frameworks
Starting from scratch for NIS2 or ENS
Reusable, reviewable answers
Frequently asked questions
Yes. The Free plan includes a complete ISO 27001 audit, an executive report in PDF and the tasks derived from the audit. You can sign up at app.audexa.es or ask us for a guided demo.
No. Certification is issued by an accredited certification body. Audexa helps you implement and maintain your ISMS and prepare the evidence and reports for the audit.
Yes. The audit follows the 2022 edition: clauses 4 to 10 and the 93 Annex A controls grouped into organizational, people, physical and technological controls.
Yes. You set the applicability of each control with its justification and export it together with the organization's context and the framework version.
Yes. Audexa includes mappings from ISO 27001 to NIS2, ENS, GDPR, NIST CSF 2.0, ISO 9001 and ISO 14001 so you can reuse evidence and reviewable answers.
No. Audexa suggests answers with their source, flags what doesn't add up and tells you which gaps raise your score the most, but a person decides every answer. Nothing is answered or submitted on its own.
It helps you prepare for it. With Sites and group (a module Audexa activates on request, for Premium and Diamond), you answer the central controls once at the main site, each site's controls come from its latest ISO 27001 audit and Audexa proposes a sample of sites based on phase and risk, with the scope statement in the report. It is guidance only: your certification body confirms the final sample.
Audexa runs on EU infrastructure, with role-based access, two-factor authentication and activity traceability.
Request a demo
In a 30-minute demo we walk through the audit, the Statement of Applicability, policies and the handover to the auditor.