
Governance
Approved and signed policies, defined roles and management oversight based on up-to-date data.
Governance · Risk · Compliance
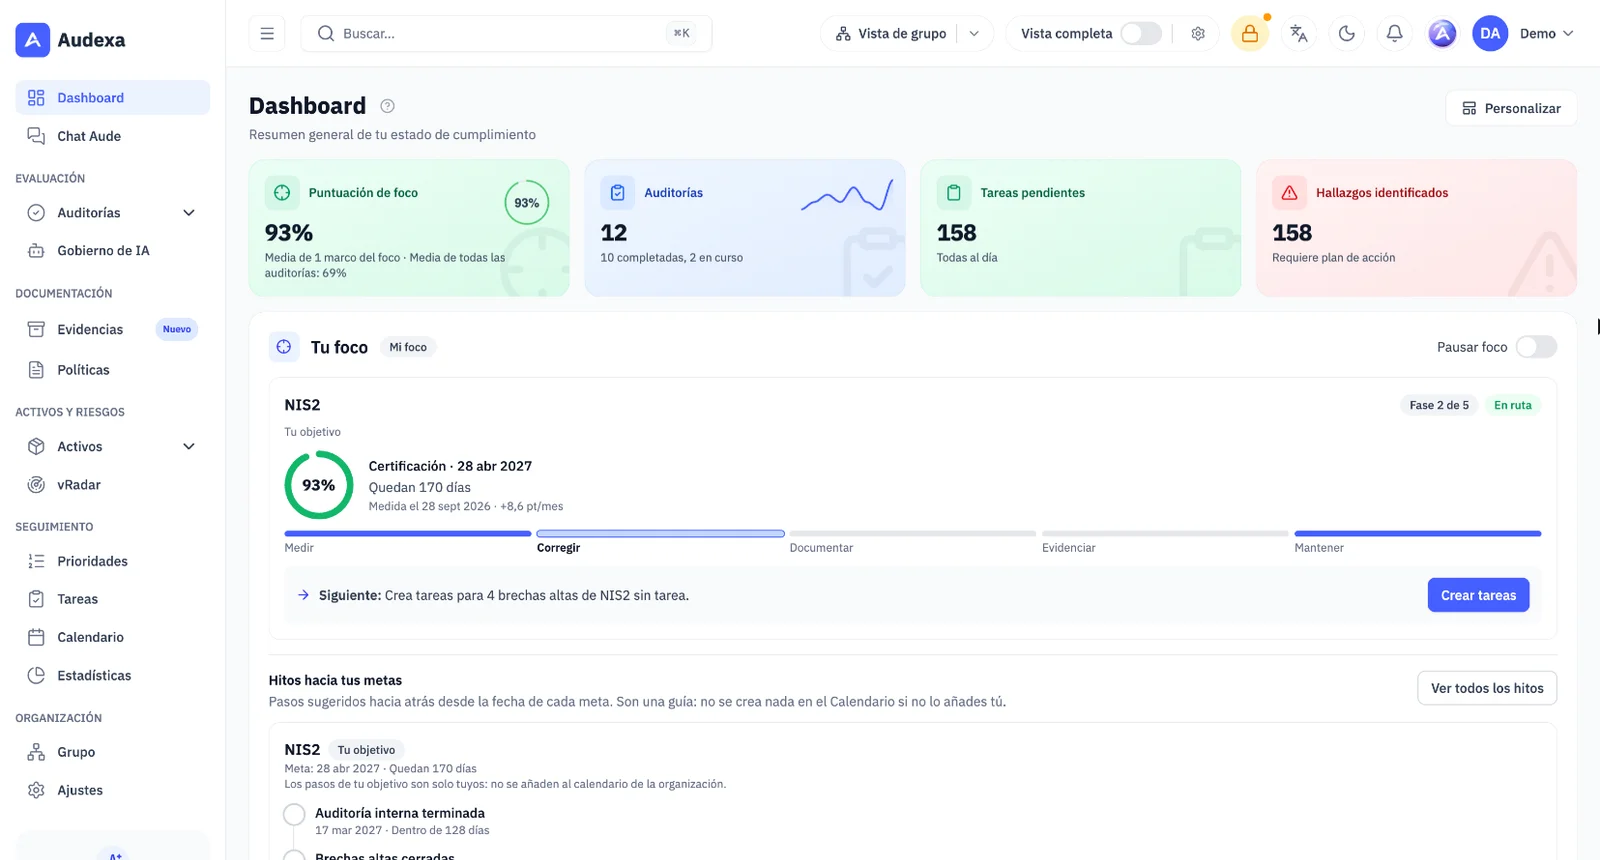
Audexa brings together audits across 22 frameworks, risk management, policies, evidence, assets and management reporting in one platform. With Focus mode it shows you only what your framework asks for and gives you a single next step; with Sites and group, you run several sites and subsidiaries from a single screen.
Why a GRC platform
Every new regulation (NIS2, DORA, the AI Act) adds requirements that overlap with the previous ones. Without a platform, the same work is repeated in every audit and management has no single view.
Approved and signed policies, defined roles and management oversight based on up-to-date data.
Risks derived from real gaps, rated by likelihood and impact, with traceable treatment and acceptance.
Audits per framework, reusable evidence and an action plan you can track and prove.
What's included
Every module shares data with the others: a piece of evidence, a risk or a task is visible from every framework it affects.
Audit and measure against each standard.
NIS2, DORA, ENS, ISO 27001, NIST CSF 2.0, SOC 2, ISO 27017, Cyber Resilience Act, TPRM, GDPR, LOPDGDD and LSSI, ISO 27701, ISO 27018, EU AI Act, ISO 42001, ISO 37301 / UNE 19601, whistleblowing channel, ISO 9001, ISO 14001, ISO 45001, ISO 20000-1 and ISO 22301.
Choose your framework and Audexa shows you only what it asks for. Your path gives you a single next step, with the reason for it and the approximate time.
Suggested answers with their source, a consistency check before submitting and how many points each gap adds. A person always decides.
Scheduled re-audits, cycle-to-cycle comparison and Statement of Applicability.
Prioritize what really matters.
Risks derived from gaps, with treatment and acceptance signed by management.
Devices, software, SaaS, suppliers and contracts with an owner and periodic review.
vRadar matches your inventory against known vulnerabilities and creates remediation tasks.
Registration, classification and obligations under the EU AI Act.
Decide, document and report.
67 templates with versions, approval and internal or link-based signing.
A private evidence vault with expiry, review and history.
Executive and technical reports in PDF, Excel and Word, plus a configurable dashboard.
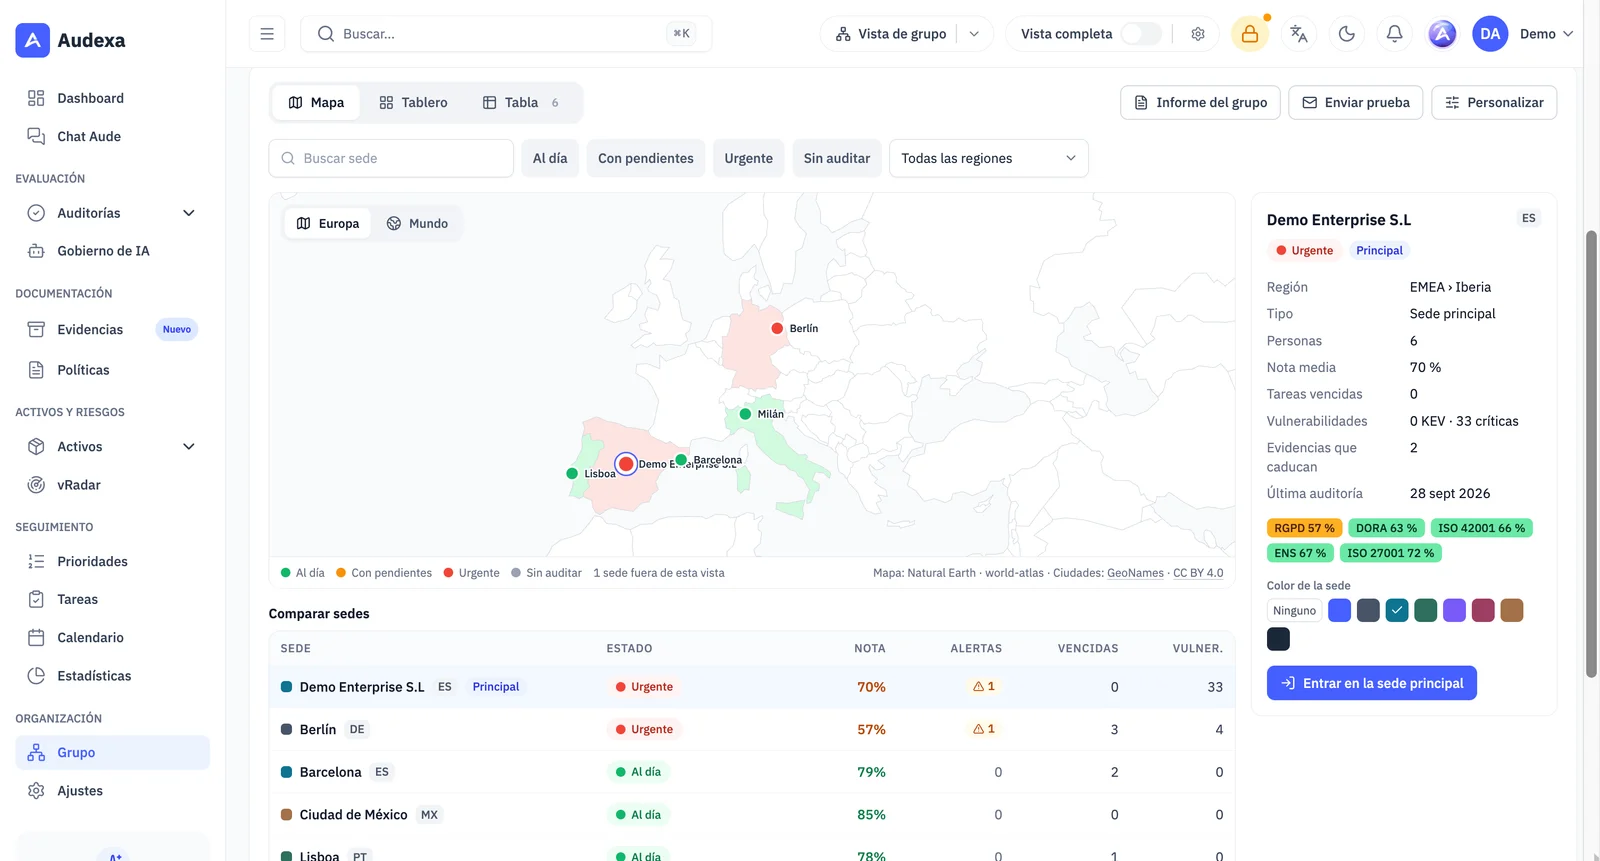
A main site with branches and subsidiaries, a group overview with a map and ranking, and custom roles by group, region or site.
Some features depend on your plan and active modules.
Focus mode
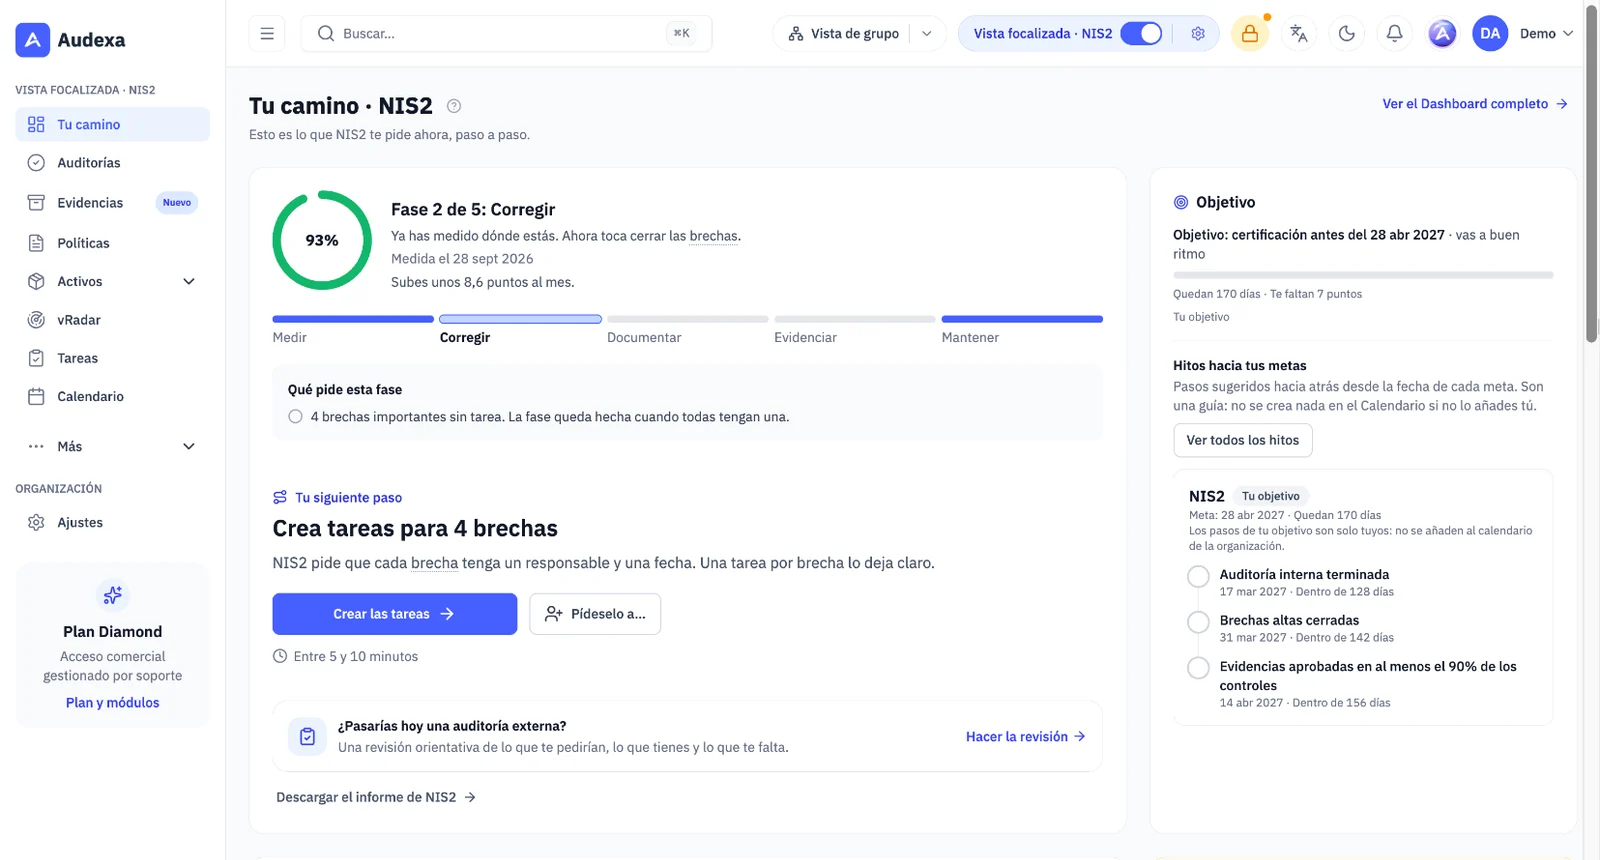
Choose the framework you want to work on, for example NIS2, and the Focused view shows you only what it asks of you. Your path is the new home page: your score, the phase you are in and a single next step. Nothing is deleted: everything else stays under More or behind See all.
Sites and group
A main site manages its sites: each branch or subsidiary keeps its own data and its own team, and works with the group's plan. Audexa activates it on request on Premium (3 sites) and Diamond (5), extendable.
Multi-framework
Cross-framework mappings let you reuse evidence and suggest reviewable answers when coverage is high. A control is never marked as compliant automatically.
Integrations
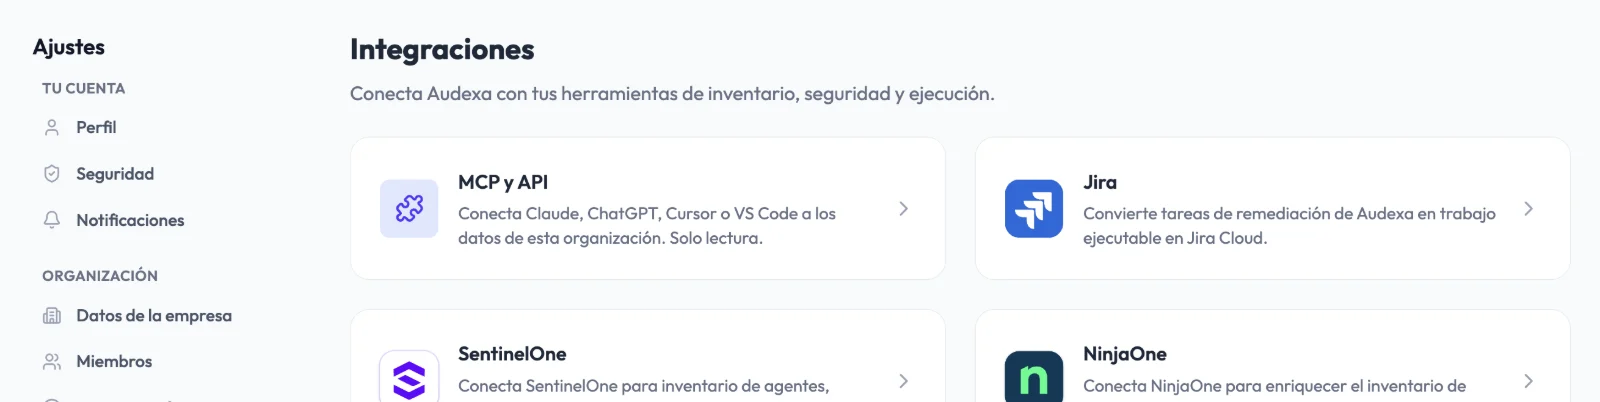
Your inventory is fed by your device management and security tools, tasks can become Jira issues, and the REST API and MCP server let you query your compliance from other systems and, with each key's permissions, create and update tasks. They never approve or delete.
How it works
Start with the most urgent standard and add the rest, reusing the work already done.
Guided audits, weighted gaps and risks rated by likelihood and impact.
Tasks with owners, signed policies, current evidence and reports for management.
Before and after
Overall view
One Excel file per standard
Dashboard covering every framework
Risks
Matrix isolated from compliance
Risks derived from real gaps
Evidence
Duplicated in every audit
One piece of evidence for several controls
Policies
Word files with no version or signature
Lifecycle with approval and signature
Reporting
Manual slide decks
Exportable executive reports
Where to start
Unordered lists of requirements
Your path with a single next step
Several sites or subsidiaries
One Excel file per site
Group overview and shared resources
Frequently asked questions
A platform that brings together governance (policies, roles, decisions), risk management and regulatory compliance so the organization manages them in a connected way rather than in isolated documents.
22 frameworks: NIS2, DORA, ENS, ISO 27001, NIST CSF 2.0, SOC 2, ISO 27017, Cyber Resilience Act, third-party risk management (TPRM), GDPR, LOPDGDD and LSSI, ISO 27701, ISO 27018, EU AI Act, ISO 42001, ISO 37301 / UNE 19601, whistleblowing channel (Spain's Law 2/2023), ISO 9001, ISO 14001, ISO 45001, ISO 20000-1 and ISO 22301, plus the AI Governance module. Framework availability depends on the plan.
No. The smart audit suggests answers with their source (evidence, other audits, assets, policies or tasks) and flags the ones that don't add up before submitting, but a person accepts or changes each one. Nothing is answered or submitted on its own.
Yes. With Sites and group, a main site manages branches and subsidiaries that keep their own data and team, shares resources and sees the status of all of them in a group overview. Audexa activates it on request on Premium (3 sites) and Diamond (5), extendable.
Not only. Audexa is designed so that a small IT, security or compliance team can run the program without relying on ongoing consulting, and it scales to organizations with several teams.
It's a web platform: you can start your first audit the same day. With Focus mode you choose your framework and Your path tells you the next step; assets, policies and evidence are loaded progressively.
Interface, frameworks, policies and reports in Spanish, English, French, Italian and German.
Audexa runs on EU infrastructure, with role-based access, two-factor authentication and activity traceability.
Request a demo
In 30 minutes we look at your starting point, the frameworks that apply to you and what your GRC program would look like in Audexa.