
Management accountability
Management bodies approve the cybersecurity risk-management measures, oversee their implementation, receive training and can be held liable for infringements.
Directive (EU) 2022/2555 · NIS2
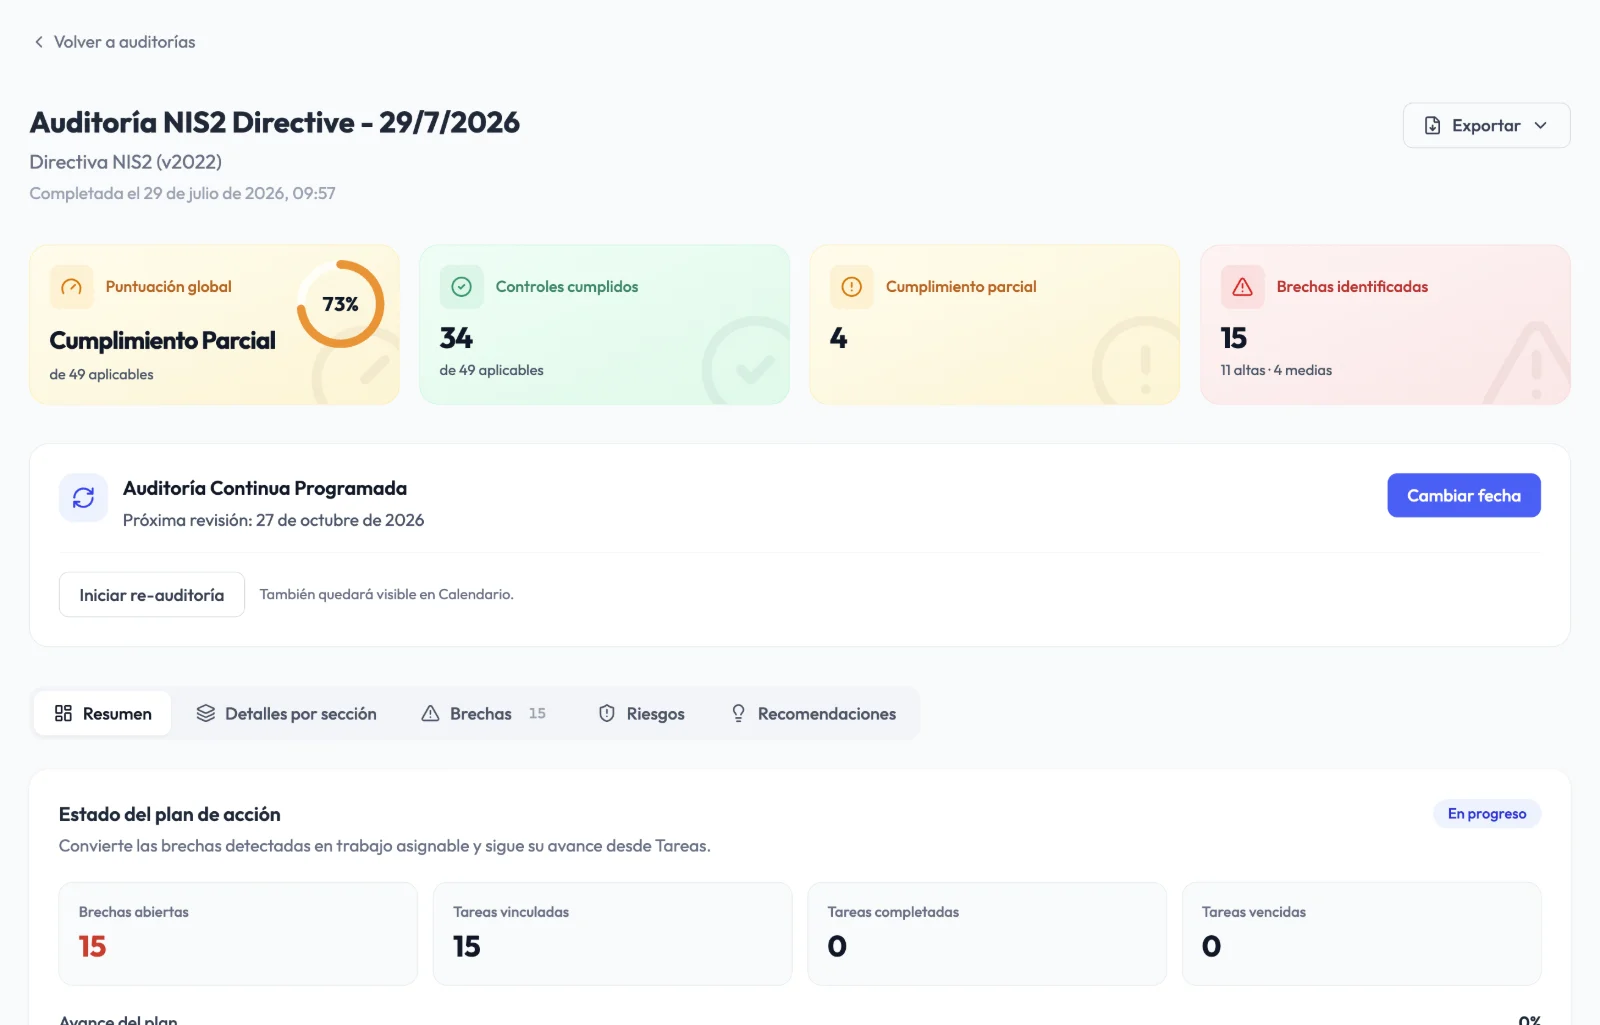
Audexa turns NIS2 into measurable work: a guided 49-control audit, gaps prioritized by risk, policies, evidence and an executive report so management can approve and oversee the measures.
What NIS2 requires
The directive expands the sectors in scope and raises the bar. Technical measures are not enough: you have to show that they are managed, reviewed and overseen by management.
Management bodies approve the cybersecurity risk-management measures, oversee their implementation, receive training and can be held liable for infringements.
Article 21 lists minimum measures, including risk analysis, incident handling, business continuity, supply chain security, secure development, encryption, access control, training and MFA.
Significant incidents require an early warning within 24 hours, an incident notification within 72 hours and a final report within one month.
The security of suppliers and service providers is part of the mandatory measures, including an assessment of their practices and vulnerabilities.
The directive sets maximum fines of at least €10 million or 2% of worldwide annual turnover for essential entities, and €7 million or 1.4% for important entities.
Authorities can request proof of compliance. A one-off audit with no follow-up leaves gaps between reviews.
Sources: Directive (EU) 2022/2555 (EUR-Lex)
How Audexa helps
One workspace to assess, prioritize, execute and report, with no scattered spreadsheets or unversioned documents.
Know where you stand on every requirement.
Each question comes with What they ask of you, Explain it to me and the NIS2 article it answers, checked against the official text.
In your first NIS2 audit, Audexa suggests the answers it already knows from your evidence, Assets, policies and other audits. You accept or change them one by one.
Mark controls as not applicable or out of scope with a justification, and export the statement of applicability.
Yes, Partial and No answers with proportional impact, so the result reflects your actual situation.
Turn every gap into work with an owner.
Create tasks from all or some gaps, with an owner, dates and expected evidence.
How much each gap raises your score and how much effort it takes, with the quick wins first in your plan toward your target.
Rate likelihood and impact, then choose to mitigate, accept or transfer, with management sign-off and approval.
Link assets and suppliers to controls and detect CVE exposure with vRadar.
Keep the proof ready for management and supervisors.
Private documents with expiry, review and history, reusable across controls and frameworks.
Editable templates with approval, signature and one-step conversion into evidence.
PDF, Excel and Word with progress over time, gaps, risks and a roadmap for management.
Some features depend on your plan and active modules.
NIS2 controls
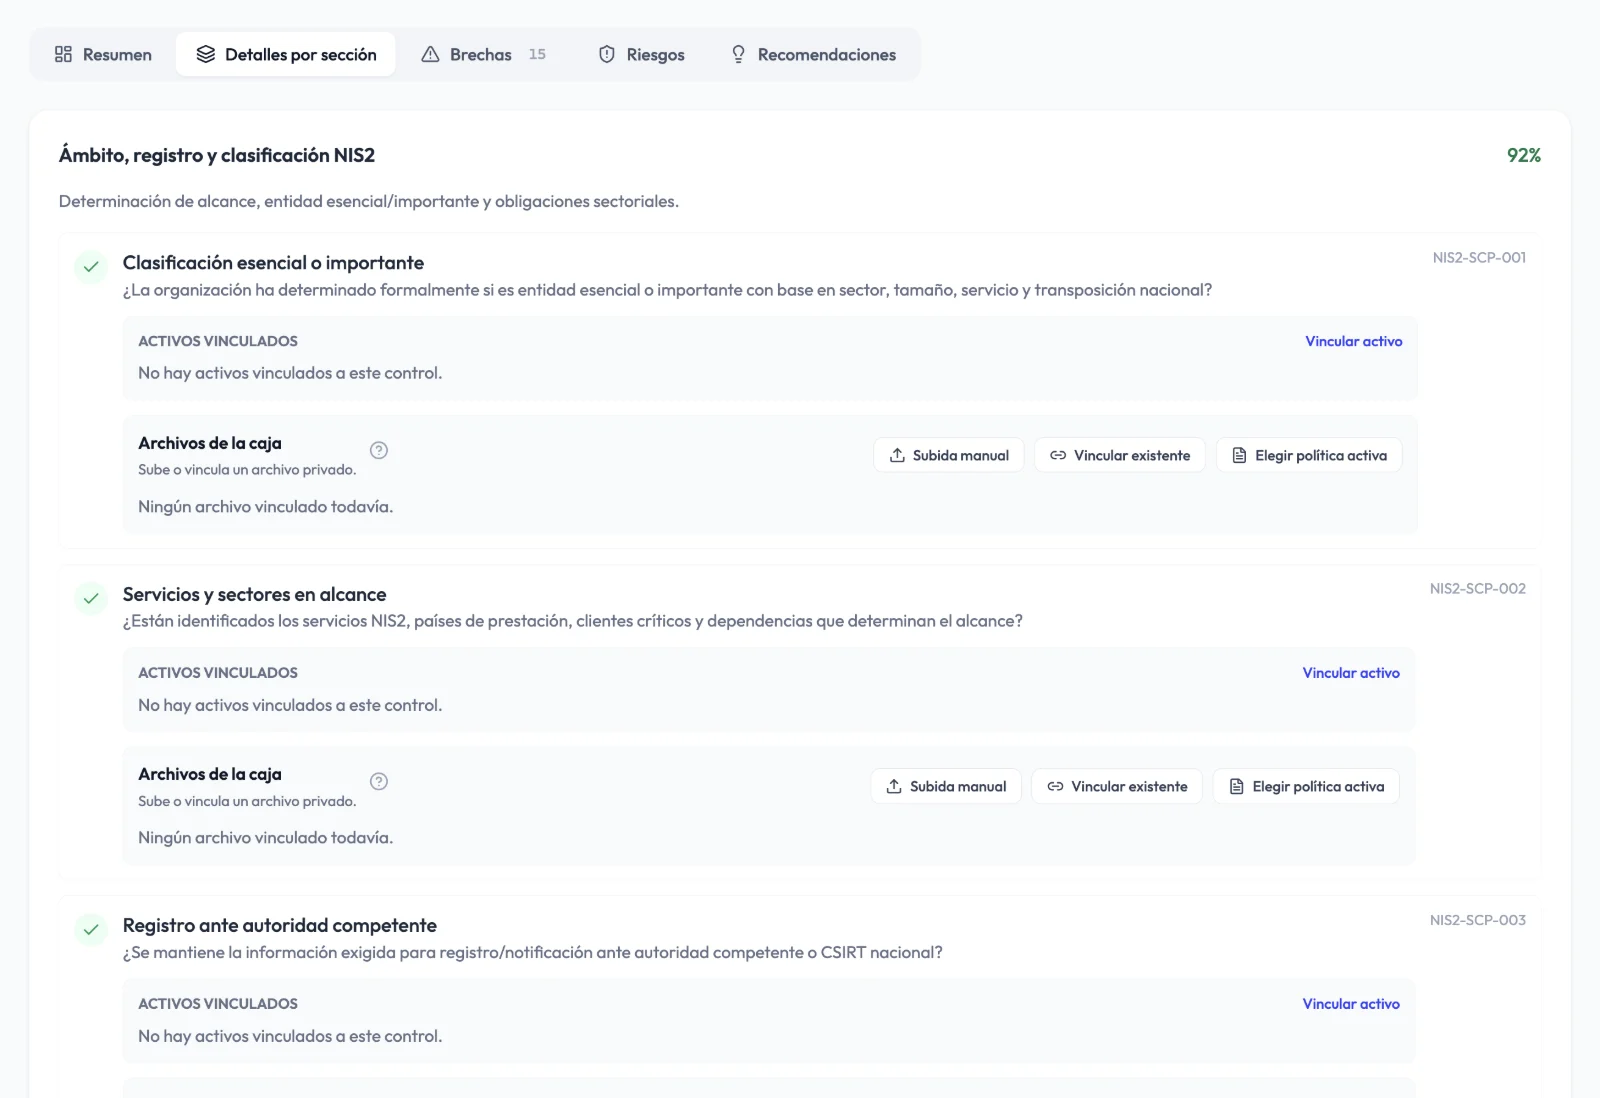
The 49 controls are organized into nine domains that follow the structure of the directive. Each one explains what to review, how to interpret it, what to do if something is missing and, when a reliable reference exists, the NIS2 article it comes from.
NIS2 policies
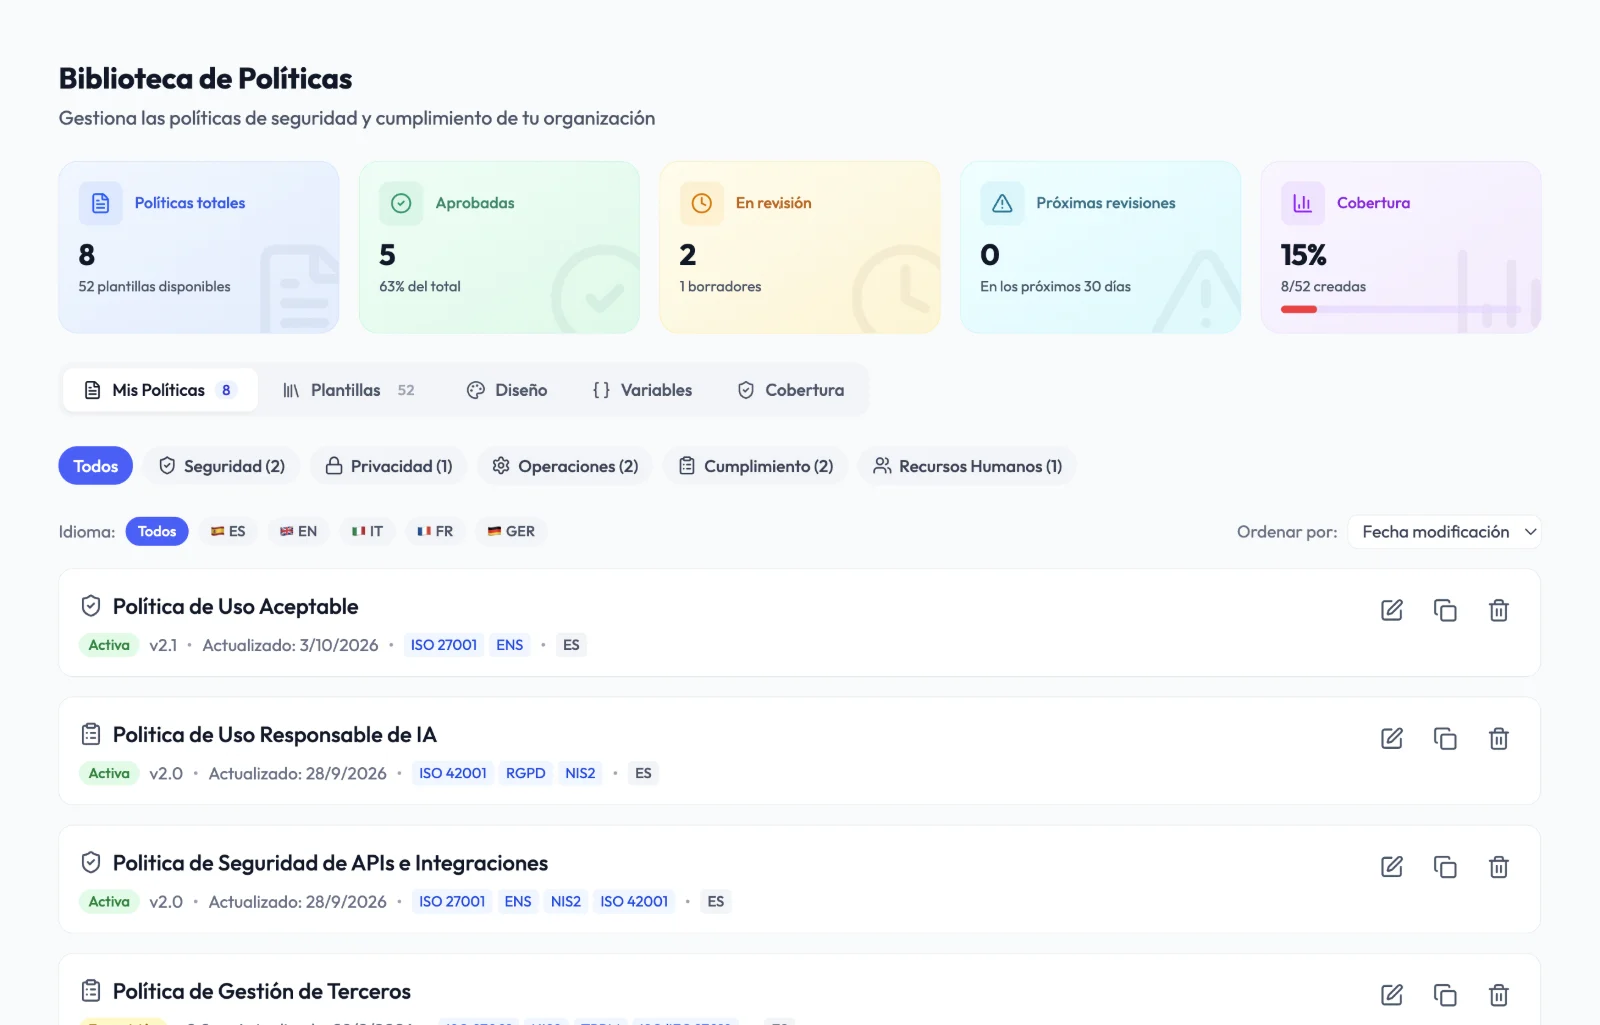
Start from security templates, tailor them with your organization's variables and manage the full lifecycle: version, review, approval and signature. An active policy can be saved as evidence for the control.
NIS2 action plan
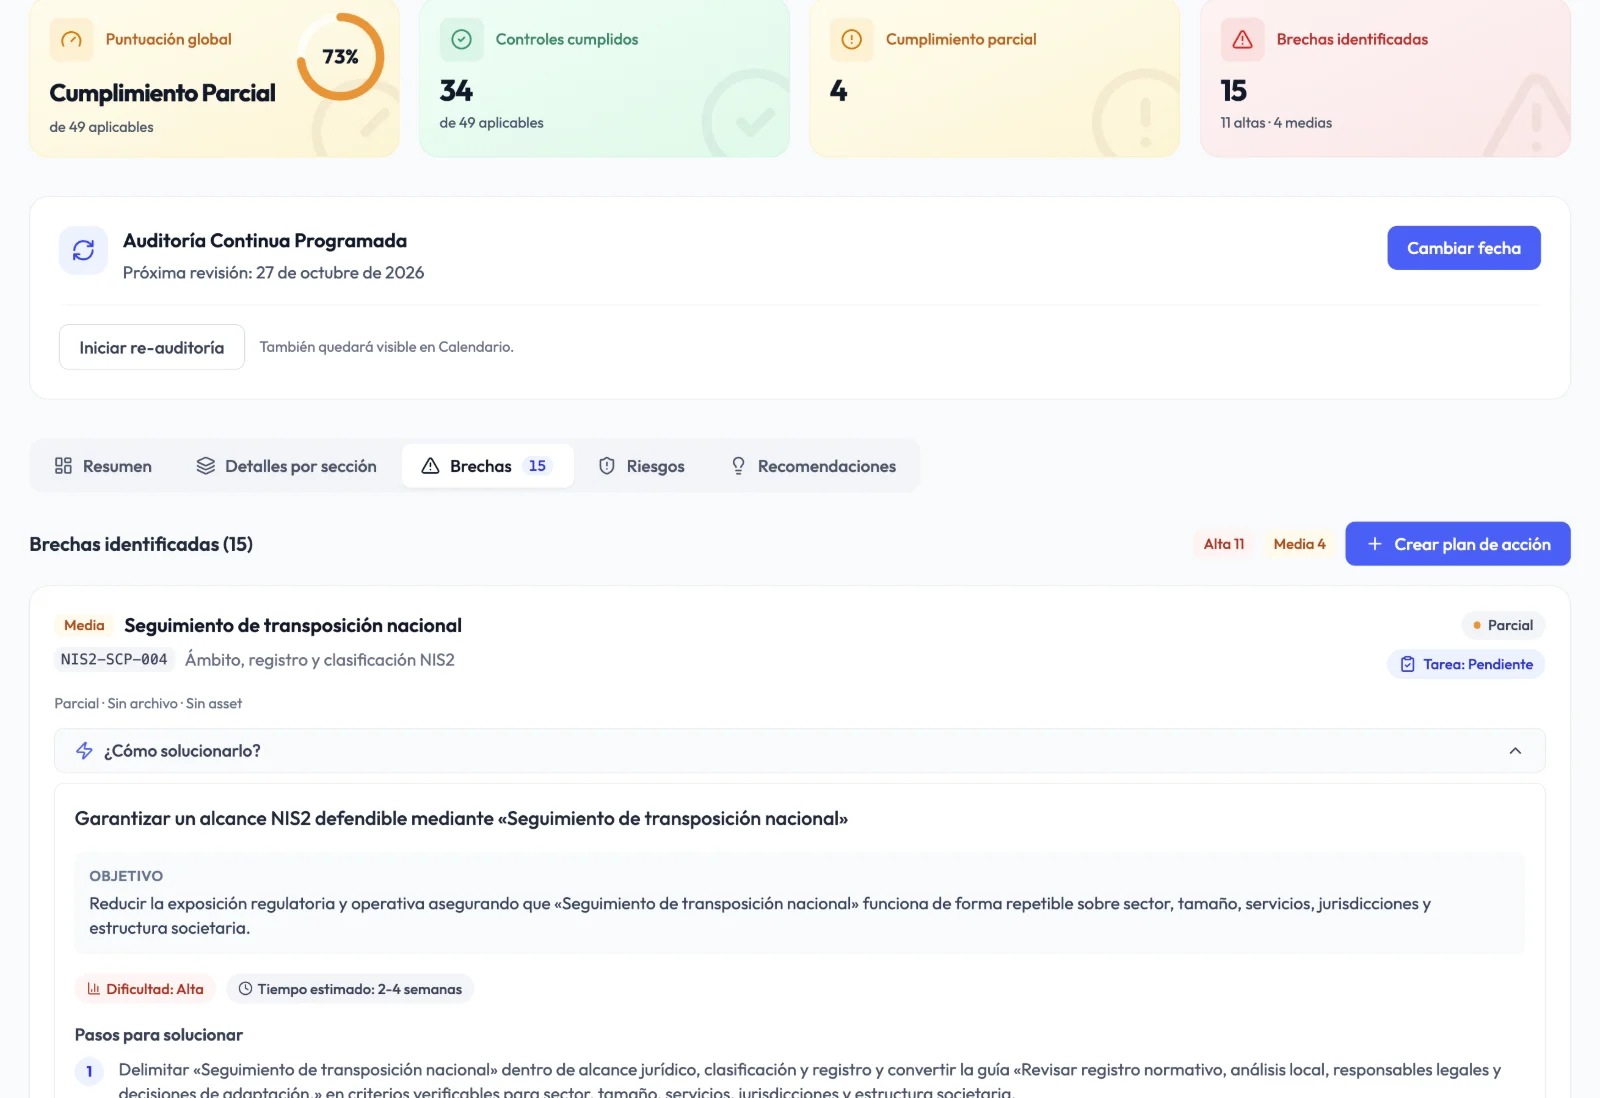
Each gap can become a task with the control's context, recommended steps and expected evidence. Completing a task does not mark the control as compliant: evidence and a re-audit confirm the progress.
Focused view
With Focus mode, the menu is reduced to what NIS2 requires of you. Your path tells you which phase you are in and gives you a single next step, with the reason for it and the approximate time. Nothing is deleted: everything else stays under More, and the Full view comes back with a switch.
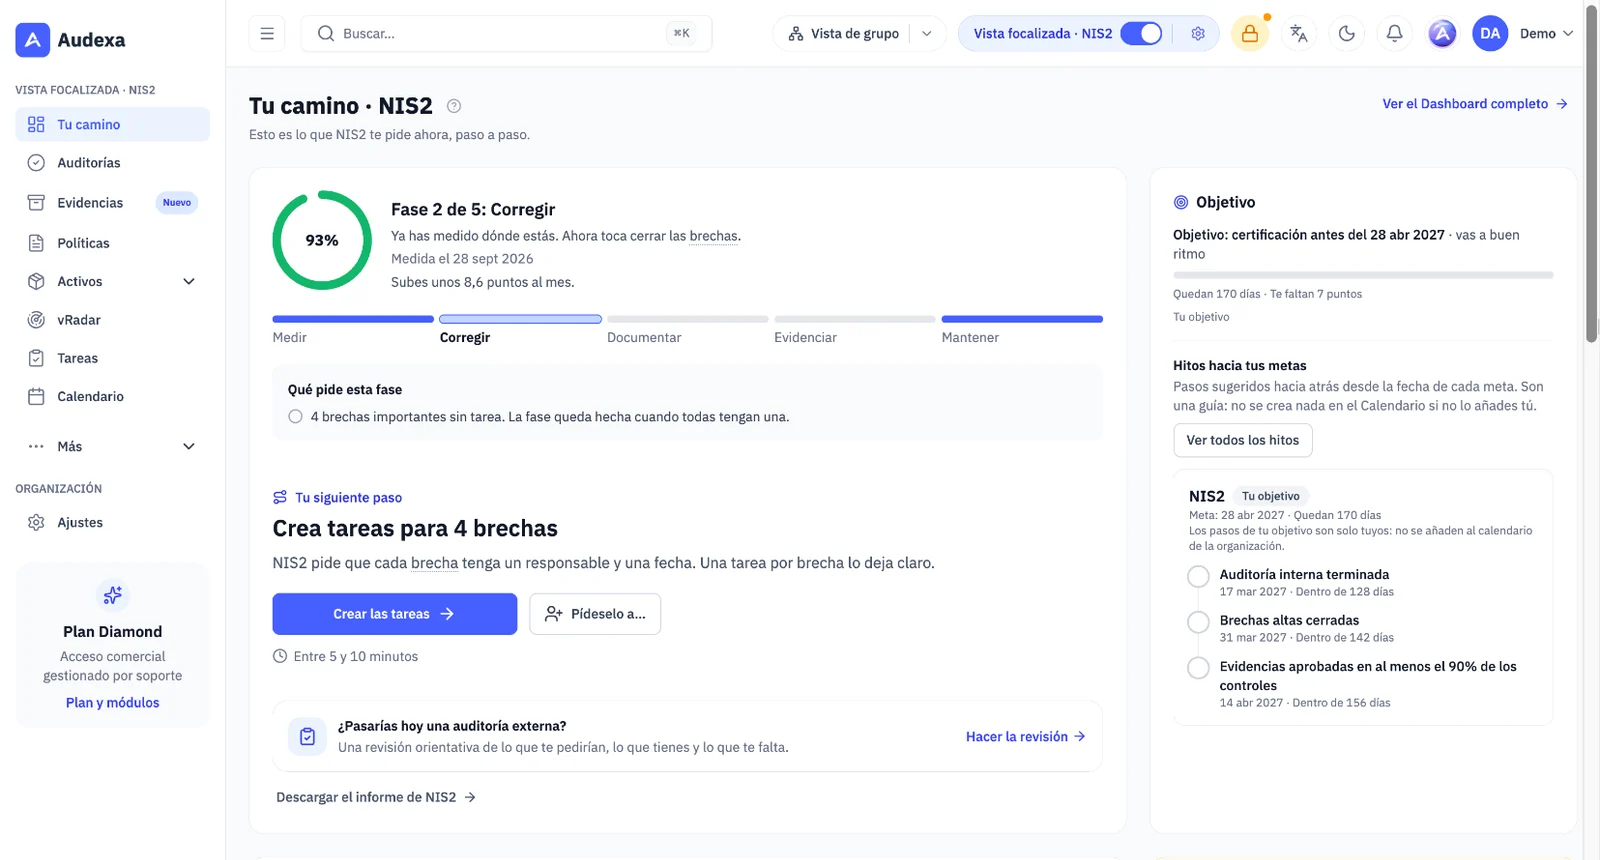
How it works
Set NIS2 as your focus, describe your organization, decide which controls apply and justify any exclusions.
Answer the NIS2 audit control by control and get your score and prioritized gaps.
Assign tasks, gather evidence, approve policies and share the report with management.
Before and after
Initial assessment
Weeks of interviews and Excel
Guided audit from day one
Gap tracking
Lists with no owner or date
Tasks with owners, deadlines and expected evidence
Evidence
Attachments scattered across email and folders
Private vault with expiry and history
Management reporting
Manual slide decks
Exportable executive report
Other frameworks
Starting from scratch for each standard
Mappings to ISO 27001 and Spain's ENS
Frequently asked questions
The directive has been in force in the EU since 2023 and the transposition deadline was October 17, 2024, but it applies through each Member State's national law, and the status and details vary by country. On July 8, 2026, the European Commission referred Ireland, Spain, France and the Netherlands to the Court of Justice of the EU for not fully transposing it. Check your national law: preparing now avoids improvising once it applies to you.
Medium-sized and large entities in the sectors listed in Annexes I and II of the directive (energy, transport, health, digital infrastructure, managed ICT services, manufacturing, food and others), and in some cases smaller entities because of their critical role. Audexa includes a dedicated domain to document scope and classification as an essential or important entity.
No. NIS2 is not a certification and Audexa does not replace the competent authority. Audexa helps you measure your alignment, carry out remediation and keep the evidence that demonstrates compliance.
No. Audexa includes 61 mappings between NIS2 and ISO 27001 so you can reuse evidence and reviewable answers across both frameworks.
You can start the guided audit the same day. Timing depends on your organization, but the results, gaps and action plan are generated as soon as you complete the questionnaire.
The NIS2 audit assesses your ability to detect, classify and report incidents within the Article 23 deadlines, and gaps become concrete tasks and policies, such as the incident reporting procedure.
No. Audexa suggests answers with their source, flags what doesn't add up and tells you which gaps raise your score the most, but a person decides every answer. Nothing is answered or submitted on its own.
Audexa runs on EU infrastructure, with role-based access, two-factor authentication and activity traceability.
Request a demo
In a 30-minute demo we walk through the NIS2 audit, the action plan and the management report, with examples from your sector.